|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA707] DSA-707-1 mysql Vulnerability Assessment Details
|
[DSA707] DSA-707-1 mysql |
||
|
DSA-707-1 mysql Detailed Explanation for this Vulnerability Assessment Several vulnerabilities have been discovered in MySQL, a popular database. The Common Vulnerabilities and Exposures project identifies the following problems: Sergei Golubchik discovered a problem in the access handling for similar named databases. If a user is granted rights to a database with a name containing an underscore ("_"), the user also gains rights to other databases with similar names. Stefano Di Paola discovered that MySQL permits remote authenticated users with INSERT and DELETE rights to execute arbitrary code by using CREATE FUNCTION to access libc calls. Stefano Di Paola discovered that MySQL permits remote authenticated users with INSERT and DELETE rights to bypass library path restrictions and execute arbitrary libraries by using INSERT INTO to modify the mysql.func table. Stefano Di Paola discovered that MySQL uses predictable file names when creating temporary tables, which permits local users with CREATE TEMPORARY TABLE rights to overwrite arbitrary files via a symlink attack. For the stable distribution (woody) these problems have been fixed in version 3.23.49-8.11. For the unstable distribution (sid) these problems have been fixed in version 4.0.24-5 of mysql-dfsg and in version 4.1.10a-6 of mysql-dfsg-4.1. We recommend that you upgrade your mysql packages. Solution : http://www.debian.org/security/2005/dsa-707 Network Security Threat Level: High Networks Security ID: 12781 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99
Samsung M391A1K43BB2-CTDQ 4 x 8GB 1Rx8 PC4-2666V DDR4 UDIMM RAM Memory
$140.00
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
Lot of 5 DDR4 Mixed Desktop RAM 28GB Total G.Skill Patriot Ballistix XPG Tested
$358.50
Crucial 32GB(4 x 8GB) CT8G4DFS824A.C8FDD1 DDR4-2400 UDIMM Desktop RAM - CR352A
$89.95
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
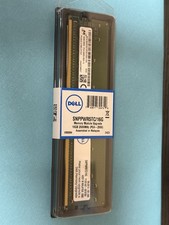
Dell 16GB PC4-21300 (DDR4-2666) Memory (SNPPWR5TC16G)
$89.99
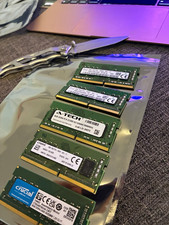
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
|
||
|
No Discussions have been posted on this vulnerability. |