|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA531] DSA-531-1 php4 Vulnerability Assessment Details
|
[DSA531] DSA-531-1 php4 |
||
|
DSA-531-1 php4 Detailed Explanation for this Vulnerability Assessment Two vulnerabilities were discovered in php4: The memory_limit functionality in PHP 4.x up to 4.3.7, and 5.x up to 5.0.0RC3, under certain conditions such as when register_globals is enabled, permits remote attackers to execute arbitrary code by triggering a memory_limit abort during execution of the zend_hash_init function and overwriting a HashTable destructor pointer before the initialization of key data structures is complete. The strip_tags function in PHP 4.x up to 4.3.7, and 5.x up to 5.0.0RC3, does not filter null (\0) characters within tag names when restricting input to permited tags, which permits dangerous tags to be processed by web browsers such as Internet Explorer and Safari, which ignore null characters and facilitate the exploitation of cross-site scripting (XSS) vulnerabilities. For the current stable distribution (woody), these problems have been fixed in version 4.1.2-7. For the unstable distribution (sid), these problems have been fixed in version 4:4.3.8-1. We recommend that you update your php4 package. Solution : http://www.debian.org/security/2004/dsa-531 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
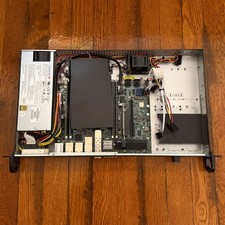
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
Supermicro 1027GR-TSF 1U Rackmount Server 2x Xeon 2.3GHz 128GB DDR3
$219.99
$280.00
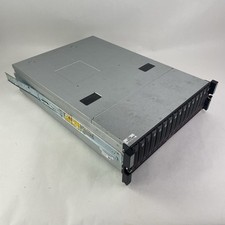
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |