|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA495] DSA-495-1 linux-kernel-2.4.16-arm Vulnerability Assessment Details
|
[DSA495] DSA-495-1 linux-kernel-2.4.16-arm |
||
|
DSA-495-1 linux-kernel-2.4.16-arm Detailed Explanation for this Vulnerability Assessment Several serious problems have been discovered in the Linux kernel. This update takes care of Linux 2.4.16 for the ARM architecture. The Common Vulnerabilities and Exposures project identifies the following problems that will be fixed with this update: The kernel module loader permits local users to gain root rights by using ptrace to attach to a child process that is spawned by the kernel. A vulnerability has been discovered in the R128 DRI driver in the Linux kernel which could potentially lead a possible hacker to gain unauthorised rights. Alan Cox and Thomas Biege developed a correction for this. Arjan van de Ven discovered a stack-based buffer overflow in the ncp_lookup function for ncpfs in the Linux kernel, which could lead a possible hacker to gain unauthorised rights. Petr Vandrovec developed a correction for this. zen-parse discovered a buffer overflow vulnerability in the ISO9660 filesystem component of Linux kernel which could be abused by a possible hacker to gain unauthorised root access. Sebastian Krahmer and Ernie Petrides developed a correction for this. Solar Designer discovered an information leak in the ext3 code of Linux. In a worst case a local attacker could obtain sensitive information (such as cryptographic keys in another worst case) which would otherwise never hit disk media. Theodore Ts'o developed a correction for this. Andreas Kies discovered a denial of service condition in the Sound Blaster driver in Linux. He also developed a correction for this. These problems are also fixed by upstream in Linux 2.4.26 and will be fixed in Linux 2.6.6. The following security matrix explains which kernel versions for which architectures are already fixed and which will be removed instead. We recommend that you upgrade your kernel packages immediately, either with a Debian provided kernel or with a self compiled one. Vulnerability matrix for CVE-2004-0109 Solution : http://www.debian.org/security/2004/dsa-495 Network Security Threat Level: High Networks Security ID: 10141, 10152, 10152, 7112, 9570, 9691, 9985 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Kingston 32GB 64GB 128GB 256GB USB 3.0 Flash Drive Thumb Memory Stick Pen lot
$285.90
Lot of 4 8GB DDR4 PC4-2400T ECC Registered Server RAM 32GB 1Rx8 RDIMM MICRON
$149.99
1/ 10/ 100pcs USB 2.0 2GB, 4GB ,8GB ,16GB ,32GB ,64GB 128GB USB Flash Drives Lot
$202.50
Microsoft Office 2021 Pro Plus USB for 1PC Windows 10 & 11
$62.55
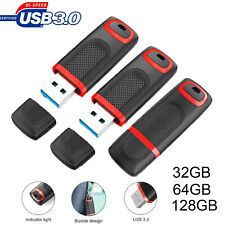
USB 3.0 Flash Drive 32GB 64GB 128GB Memory Stick Thumb Stick Lot Pack
$826.09
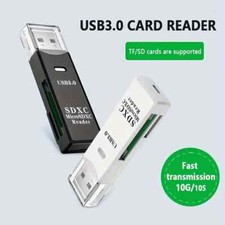
USB 3.0 Micro SD SDHC TF Card Reader Memory Adapter for PC Laptop Camera lot
$3.75
Samsung M391A1K43BB2-CTDQ 4 x 8GB 1Rx8 PC4-2666V DDR4 UDIMM RAM Memory
$140.00
Server Memory: Samsung 32GB 4DRx4 PC4-2133P ECC LRDIMM DDR4 M386A4G40DM0-CPB
$124.95
4x8GB Samsung DDR4 2133MHz PC4-2133P 1Rx4 ECC Registered Server RAM 32GB Sansumg
$149.99
TF/SD Card Adapter Camera Reader Android Type-c For iPhone17 Pro Max Plusm lot
$573.98
|
||
|
No Discussions have been posted on this vulnerability. |