|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA480] DSA-480-1 linux-kernel-2.4.17+2.4.18-hppa Vulnerability Assessment Details
|
[DSA480] DSA-480-1 linux-kernel-2.4.17+2.4.18-hppa |
||
|
DSA-480-1 linux-kernel-2.4.17+2.4.18-hppa Detailed Explanation for this Vulnerability Assessment Several serious problems have been discovered in the Linux kernel. This update takes care of Linux 2.4.17 and 2.4.18 for the hppa (PA-RISC) architecture. The Common Vulnerabilities and Exposures project identifies the following problems that will be fixed with this update: A vulnerability has been discovered in the R128 DRI driver in the Linux kernel which could potentially lead a possible hacker to gain unauthorised rights. Alan Cox and Thomas Biege developed a correction for this. Arjan van de Ven discovered a stack-based buffer overflow in the ncp_lookup function for ncpfs in the Linux kernel, which could lead a possible hacker to gain unauthorised rights. Petr Vandrovec developed a correction for this. zen-parse discovered a buffer overflow vulnerability in the ISO9660 filesystem component of Linux kernel which could be abused by a possible hacker to gain unauthorised root access. Sebastian Krahmer and Ernie Petrides developed a correction for this. Solar Designer discovered an information leak in the ext3 code of Linux. In a worst case a possible hacker could read sensitive data such as cryptographic keys which would otherwise never hit disk media. Theodore Ts'o developed a correction for this. Andreas Kies discovered a denial of service condition in the Sound Blaster driver in Linux. He also developed a correction for this. These problems are also fixed by upstream in Linux 2.4.26 and will be fixed in Linux 2.6.6. For the stable distribution (woody) these problems have been fixed in version 32.4 for Linux 2.4.17 and in version 62.3 for Linux 2.4.18. For the unstable distribution (sid) these problems will be fixed soon. We recommend that you upgrade your kernel packages immediately, either with a Debian provided kernel or with a self compiled one. Vulnerability matrix for CVE-2004-0109 Solution : http://www.debian.org/security/2004/dsa-480 Network Security Threat Level: High Networks Security ID: 10152 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

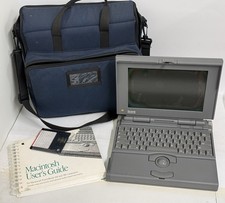
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
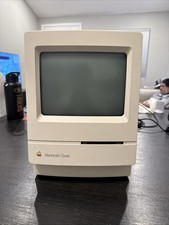
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
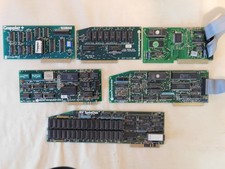
Apple Computer cards VTG 670-8020-B 607-0103-C 607-0291-C AST -Orange Micro ++
$169.00
READ - Vintage Apple Macintosh SE/30 - Boots
$850.00
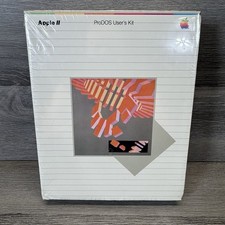
Vintage 1983 Apple II ProDOS User's Kit Computer Software NEW SEALED A2D2010
$64.95
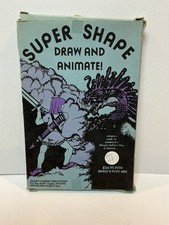
Vintage Apple II Avant-Garde Creations Super Shape Draw And Animate 1981
$295.00
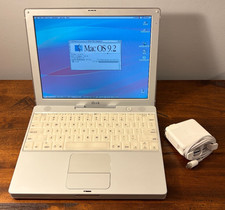
Vintage Apple iBook G3 12.1” 500MHz 2001 Restored, SSD Upgraded Mac OS 9.2/OS X
$180.00
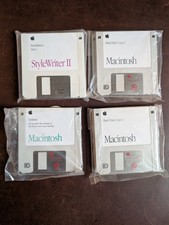
Vintage 1992 Mac System 7.1P1 Apple Software 3.5” Floppy Disks NOS
$35.00
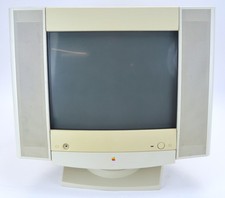
Vintage Apple Multiple Scan 15av Display Monitor M4681
$299.99
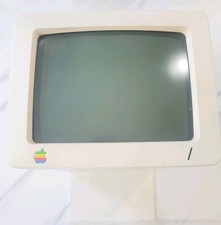
Vintage Apple Monitor IIc 9" Green Monochrome 06/1985 A2M4090 October 1984 Stand
$275.00
|
||
|
No Discussions have been posted on this vulnerability. |