|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA475] DSA-475-1 linux-kernel-2.4.18-hppa Vulnerability Assessment Details
|
[DSA475] DSA-475-1 linux-kernel-2.4.18-hppa |
||
|
DSA-475-1 linux-kernel-2.4.18-hppa Detailed Explanation for this Vulnerability Assessment Several local root exploits have been discovered recently in the Linux kernel. This security advisory updates the PA-RISC kernel 2.4.18 for Debian GNU/Linux. The Common Vulnerabilities and Exposures project identifies the following problems that are fixed with this update: An integer overflow in brk() system call (do_brk() function) for Linux permits a local attacker to gain root rights. Fixed upstream in Linux 2.4.23. Paul Starzetz discovered a flaw in bounds checking in mremap() in the Linux kernel (present in version 2.4.x and 2.6.x) which may permit a local attacker to gain root rights. Version 2.2 is not affected by this bug. Fixed upstream in Linux 2.4.24. Paul Starzetz and Wojciech Purczynski of isec.pl discovered a critical security vulnerability in the memory management code of Linux inside the mremap(2) system call. Due to missing function return value check of internal functions a local attacker can gain root rights. Fixed upstream in Linux 2.4.25 and 2.6.3. Please note that the source package has to include a lot of updates in order to compile the package, which wasn't possible with the old source package. For the stable distribution (woody) these problems have been fixed in version 62.1 of kernel-image-2.4.18-hppa. For the unstable distribution (sid) these problems have been fixed in version 2.4.25-1 of kernel-image-2.4.25-hppa. We recommend that you upgrade your Linux kernel packages immediately. Solution : http://www.debian.org/security/2004/dsa-475 Network Security Threat Level: High Networks Security ID: 9138, 9356, 9686 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |


Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00
Dell PowerEdge FC430 Blade Server 2x Xeon E5-2630v4 20 Cores FX2 FX2s No RAM/HDD
$119.99
Dell PowerEdge M630 Blade Server 2x Xeon E5-2680 v4, 2F3MP , 4GDP5 ,R10KJ ,JVFVR
$95.20
Dell PowerEdge M620 Blade Server 2x Xeon E5-2680v2 2.8ghz 20-Cores | 128GB
$149.99
NETAPP HCI NAF-1701 SuperMicro Server 4X BLADE H410C 8X GOLD 5120 4 NODE SERVER
$1499.97
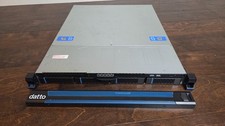
Datto S4P10 1U Blade Rack Server Intel Xeon D-2143IT 2.20GHz 48GB DDR4 4-Bay PSU
$229.95
Dell Poweredge C6400 24x 2.5’’ 2x 2400W 4x C6420 Nodes H330 | 2x SFP | 8x Trays
$799.99
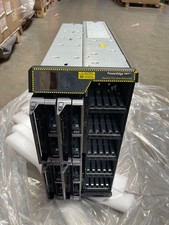
Dell PowerEdge VRTX 2.5"x25 Bay Blade Enclosure 4x1600W + 4X M640 (4X Blades)
$1599.99
Dell PowerEdge M640 Blade Barebone Server Dell P/N: HHB006 Tested Working
$149.99
Dell Poweredge VRTX 25Bay 2.5" 2x PERC 8, 2xCMC, I/O 1GB Pass Through, 4x PS
$578.08
|
||
|
No Discussions have been posted on this vulnerability. |