|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA442] DSA-442-1 linux-kernel-2.4.17-s390 Vulnerability Assessment Details
|
[DSA442] DSA-442-1 linux-kernel-2.4.17-s390 |
||
|
DSA-442-1 linux-kernel-2.4.17-s390 Detailed Explanation for this Vulnerability Assessment Several security related problems have been fixed in the Linux kernel 2.4.17 used for the S/390 architecture, mostly by backporting fixes from 2.4.18 and incorporating recent security fixes. The corrections are listed below with the identification from the Common Vulnerabilities and Exposures (CVE) project: The iBCS routines in arch/i386/kernel/traps.c for Linux kernels 2.4.18 and earlier on x86 systems permit local users to kill arbitrary processes via a binary compatibility interface (lcall). Multiple ethernet network interface card (NIC) device drivers do not pad frames with null bytes, which permits remote attackers to obtain information from previous packets or kernel memory by using malformed packets, as demonstrated by Etherleak. The route cache implementation in Linux 2.4, and the Netfilter IP conntrack module, permits remote attackers to cause a denial of service (CPU consumption) via packets with forged source addresses that cause a large number of hash table collisions related to the PREROUTING chain. The ioperm system call in Linux kernel 2.4.20 and earlier does not properly restrict rights, which permits local users to gain read or write access to certain I/O ports. A vulnerability in the TTY layer of the Linux kernel 2.4 permits attackers to cause a denial of service ("kernel oops"). The mxcsr code in Linux kernel 2.4 permits attackers to modify CPU state registers via a malformed address. The TCP/IP fragment reassembly handling in the Linux kernel 2.4 permits remote attackers to cause a denial of service (CPU consumption) via certain packets that cause a large number of hash table collisions. An integer overflow in brk() system call (do_brk() function) for Linux permits a local attacker to gain root rights. Fixed upstream in Linux 2.4.23. Paul Starzetz discovered a flaw in bounds checking in mremap() in the Linux kernel (present in version 2.4.x and 2.6.x) which may permit a local attacker to gain root rights. Version 2.2 is not affected by this bug. Fixed upstream in Linux 2.4.24. Paul Starzetz and Wojciech Purczynski of isec.pl critical security vulnerability in the memory management code of Linux inside the mremap(2) system call. Due to missing function return value check of internal functions a local attacker can gain root rights. Fixed upstream in Linux 2.4.25 and 2.6.3. For the stable distribution (woody) these problems have been fixed in version 2.4.17-2.woody.3 of s390 images and in version 0.0.20020816-0.woody.2 of the patch packages. For the unstable distribution (sid) these problems will be fixed soon. We recommend that you upgrade your Linux kernel packages immediately. Vulnerability matrix for CVE-2004-0077 Solution : http://www.debian.org/security/2004/dsa-442 Network Security Threat Level: High Networks Security ID: 4259, 6535, 7600, 7601, 7791, 7793, 7797 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Dell 6P85J 4TB ST4000NM0063 7.2k 6Gb/s 3.5” SAS SED Hard Drive with Tray
$39.99
Western Digital HUS726T4TAL5204 4TB 7.2K SAS 12Gb/s 3.5" 512e HDD NetApp X375A
$64.00

Western Digital 1TB 3.5" SATA III 7200RPM Desktop Hard Drive
$34.99
DELL 2TB Enterprise HDD (7200RPM, 3.5", SATA III, 128MB Cache) HUS722T2TALA600
$49.95
Seagate Exos ST20000NM003C 20TB CMR 7200RPM SATA6Gb/s 3.5" Enterprise Hard Drive
$509.99
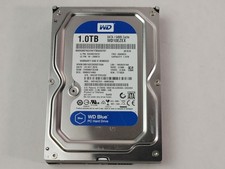
Western Digital WD Blue WD10EZEX 1 TB 3.5" SATA III Desktop Hard Drive
$23.99
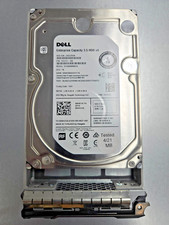
Dell ST6000NM0034 1HT27Z-150 NWCCG 6TB SAS 3.5 7.2K ENTERPRISE SERVER DRIVE
$68.99
Seagate Exos ST2000NX0253 HDD 2TB SATA 7.2K 2.5" 512b/s
$55.00
(ST8000NM0045) SEAGATE ENTERPRISE 8TB 7200RPM 4Kn SATA 6Gb/s 3.5" HARD DRIVE
$199.99

Seagate ST12000NM0127 12TB 256MB 7200RPM 3.5" SATA 6.0Gb/s Enterprise Hard Drive
$318.99
|
||
|
No Discussions have been posted on this vulnerability. |