|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA440] DSA-440-1 linux-kernel-2.4.17-powerpc-apus Vulnerability Assessment Details
|
[DSA440] DSA-440-1 linux-kernel-2.4.17-powerpc-apus |
||
|
DSA-440-1 linux-kernel-2.4.17-powerpc-apus Detailed Explanation for this Vulnerability Assessment Several local root exploits have been discovered recently in the Linux kernel. This security advisory updates the PowerPC/Apus kernel for Debian GNU/Linux. The Common Vulnerabilities and Exposures project identifies the following problems that are fixed with this update: An integer overflow in brk() system call (do_brk() function) for Linux permits a local attacker to gain root rights. Fixed upstream in Linux 2.4.23. Paul Starzetz discovered a flaw in bounds checking in mremap() in the Linux kernel (present in version 2.4.x and 2.6.x) which may permit a local attacker to gain root rights. Version 2.2 is not affected by this bug. Fixed upstream in Linux 2.4.24. Paul Starzetz and Wojciech Purczynski of isec.pl critical security vulnerability in the memory management code of Linux inside the mremap(2) system call. Due to missing function return value check of internal functions a local attacker can gain root rights. Fixed upstream in Linux 2.4.25 and 2.6.3. For the stable distribution (woody) these problems have been fixed in version 2.4.17-4 of powerpc/apus images. Other architectures will probably be mentioned in a separate advisory or are not affected (m68k). For the unstable distribution (sid) these problems will be fixed soon. We recommend that you upgrade your Linux kernel packages immediately. Solution : http://www.debian.org/security/2004/dsa-440 Network Security Threat Level: High Networks Security ID: 9686 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

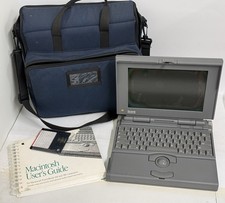
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
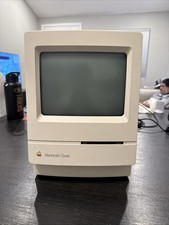
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
READ - Vintage Apple Macintosh SE/30 - Boots
$850.00
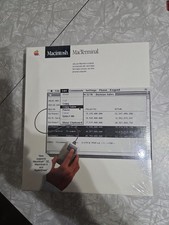
Macintosh MacTerminal M0521 Version 1.0. Vintage Apple software 1984 Sealed
$129.99
Vintage 1983 Apple II ProDOS User's Kit Computer Software NEW SEALED A2D2010
$64.95
Apple Computer cards VTG 670-8020-B 607-0103-C 607-0291-C AST -Orange Micro ++
$169.00
Vintage Apple II Avant-Garde Creations Super Shape Draw And Animate 1981
$295.00
Vintage Apple iBook G3 12.1” 500MHz 2001 Restored, SSD Upgraded Mac OS 9.2/OS X
$180.00
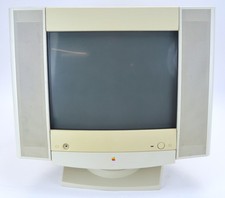
Vintage Apple Multiple Scan 15av Display Monitor M4681
$299.99
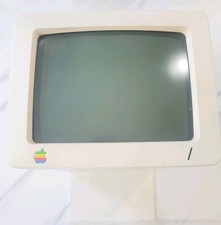
Vintage Apple Monitor IIc 9" Green Monochrome 06/1985 A2M4090 October 1984 Stand
$275.00
|
||
|
No Discussions have been posted on this vulnerability. |