|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA434] DSA-434-1 gaim Vulnerability Assessment Details
|
[DSA434] DSA-434-1 gaim |
||
|
DSA-434-1 gaim Detailed Explanation for this Vulnerability Assessment Stefan Esser discovered several security related problems in Gaim, a multi-protocol instant messaging client. Not all of them are applicable for the version in Debian stable, but affected the version in the unstable distribution at least. The problems were grouped for the Common Vulnerabilities and Exposures as follows: When the Yahoo Messenger handler decodes an octal value for email notification functions two different kinds of overflows can be triggered. When the MIME decoder decoded a quoted printable encoded string for email notification two other different kinds of overflows can be triggered. These problems only affect the version in the unstable distribution. When parsing the cookies within the HTTP reply header of a Yahoo web connection a buffer overflow can happen. When parsing the Yahoo Login Webpage the YMSG protocol overflows stack buffers if the web page returns oversized values. When splitting a URL into its parts a stack overflow can be caused. These problems only affect the version in the unstable distribution. When an oversized keyname is read from a Yahoo Messenger packet a stack overflow can be triggered. When Gaim is setup to use an HTTP proxy for connecting to the server a malicious HTTP proxy can exploit it. These problems affect all versions Debian ships. However, the connection to Yahoo doesn't work in the version in Debian stable. Internally data is copied between two tokens into a fixed size stack buffer without a size check. This only affects the version of gaim in the unstable distribution. When allocating memory for AIM/Oscar DirectIM packets an integer overflow can happen, resulting in a heap overflow. This only affects the version of gaim in the unstable distribution. For the stable distribution (woody) these problems has been fixed in version 0.58-2.4. For the unstable distribution (sid) these problems has been fixed in version 0.75-2. We recommend that you upgrade your gaim packages. Solution : http://www.debian.org/security/2004/dsa-434 Network Security Threat Level: High Networks Security ID: 9489 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

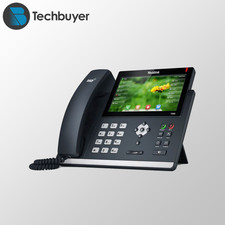
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Grandstream GXW4224 24-Line FXS Analog VoIP Gateway, Ethernet RJ-45 Black
$165.00
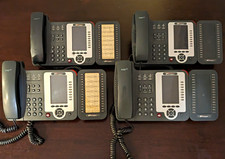
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
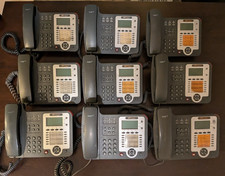
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
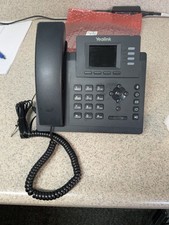
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
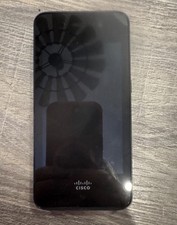
NEW Cisco CP-840 Wireless WiFi IP VoIP Phone 840 w Battery Charger Cable
$800.00
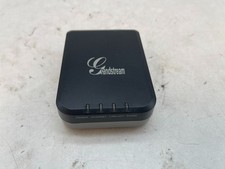
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
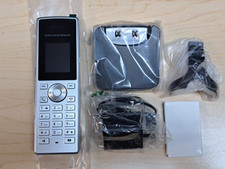
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28
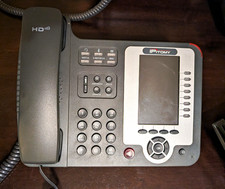
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
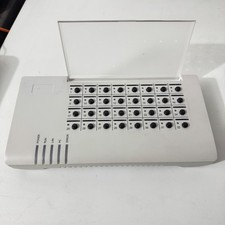
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |