|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA404] DSA-404-1 rsync Vulnerability Assessment Details
|
[DSA404] DSA-404-1 rsync |
||
|
DSA-404-1 rsync Detailed Explanation for this Vulnerability Assessment The rsync team has received evidence that a vulnerability in all versions of rsync prior to 2.5.7, a fast remote file copy program, was recently used in combination with a Linux kernel vulnerability to compromise the security of a public rsync server. While this heap overflow vulnerability could not be used by itself to obtain root access on an rsync server, it could be used in combination with the recently announced do_brk() vulnerability in the Linux kernel to produce a full remote compromise. Please note that this vulnerability only affects the use of rsync as an "rsync server". To see if you are running a rsync server you should use the command "netstat -a -n" to see if you are listening on TCP port 873. If you are not listening on TCP port 873 then you are not running an rsync server. For the stable distribution (woody) this problem has been fixed in version 2.5.5-0.2. For the unstable distribution (sid) this problem has been fixed in version 2.5.6-1.1. However, since the Debian infrastructure is not yet fully functional after the recent break-in, packages for the unstable distribution are not able to enter the archive for a while. Hence they were placed in Joey's home directory on the security machine. We recommend that you upgrade your rsync package immediately if you are providing remote sync services. If you are running testing and provide remote sync services please use the packages for woody. Solution : http://www.debian.org/security/2003/dsa-404 Network Security Threat Level: High Networks Security ID: 9153 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Lenovo ThinkPad E14 Gen 2 Laptop 14” HD Ryzen 5 16GB RAM 512GB SSD Win 11 Pro
$334.99
Lenovo ThinkPad L15 Gen 3 15.6" 16GB, Thunder Black
$241.50
Lenovo ThinkPad E14 Gen 3 Laptop 14” FHD AMD Ryzen 5 16GB RAM 512GB SSD Win 11
$374.99
Lenovo Thinkbook 14s Yoga ITL 14” Core i7-1165G7, 16GB RAM, 512GB SSD Touch
$379.00
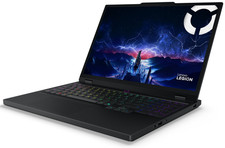
Lenovo Legion 5 Gaming 15.1" WQXGA OLED 165Hz Core i9-14900HX 16GB 1TB RTX 5070
$1469.00
Lenovo ThinkPad T14 Gen 1 14" AMD Ryzen 5 16GB 256GB SSD
$219.99
Lenovo ThinkPad X13 Gen 1 i5-10310U 16GB 512GB SSD Touch Win 11 Pro Good
$222.99
Lenovo - IdeaPad Slim 3i 15.3" 2K Touchscreen Laptop - Intel Core 7 350 2026 ...
$679.99
Lenovo ThinkPad L15 Gen 3 15.6" 16GB, Thunder Black
$241.50
Lenovo ThinkPad T14s Laptop 14” Laptop Core i5 8GB RAM 256GB SSD Windows 11 Pro
$249.99
|
||
|
No Discussions have been posted on this vulnerability. |