|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA380] DSA-380-1 xfree86 Vulnerability Assessment Details
|
[DSA380] DSA-380-1 xfree86 |
||
|
DSA-380-1 xfree86 Detailed Explanation for this Vulnerability Assessment Four vulnerabilities have been discovered in XFree86. The xterm package provides a terminal escape sequence that reports the window title by injecting it into the input buffer of the terminal window, as if the user had typed it. A possible hacker can craft an escape sequence that sets the title of a victim's xterm window to an arbitrary string (such as a shell command) and then reports that title. If the victim is at a shell prompt when this is done, the injected command will appear on the command line, ready to be run. Since it is not possible to embed a carriage return in the window title, the attacker would have to convince the victim to press Enter (or rely upon the victim's careless or confusion) for the shell or other interactive process to interpret the window title as user input. It is conceivable that the attacker could craft other escape sequences that might convince the victim to accept the injected input, however. The Common Vulnerabilities and Exposures project at cve.mitre.org has assigned the name CVE-2003-0063 to this issue. To acertain whether your version of xterm is vulnerable to abuse of the window title reporting feature, run the following command at a shell prompt from within an xterm window: (The terminal bell may ring, and the window title may be prefixed with an "l".) This flaw is exploitable by anything that can send output to a terminal window, such as a text document. The xterm user has to take action to cause the escape sequence to be sent, however (such as by viewing a malicious text document with the "cat" command). Whether you are likely to be exposed to it depends on how you use xterm. Consider the following: Debian has resolved this problem by disabling the window title reporting escape sequence in xterm it is understood but ignored. The escape sequence to set the window title has not been disabled. A future release of the xterm package will have a configuration option to permit the user to turn the window title reporting feature back on, but it will default off. The xterm package, since it emulates DEC VT-series text terminals, emulates a feature of DEC VT terminals known as "User-Defined Keys" (UDK for short). There is a bug in xterm's handling of DEC UDK escape sequences, however, and an ill-formed one can cause the xterm process to enter a tight loop. This causes the process to "spin", consuming CPU cycles uselessly, and refusing to handle signals (such as efforts to kill the process or close the window). To acertain whether your version of xterm is vulnerable to this attack, run the following command at a shell prompt from within a "sacrificial" xterm window (i.e., one that doesn't have anything in the scrollback buffer you might need to see later): This flaw is exploitable by anything that can send output to a terminal window, such as a text document. The xterm user has to take action to cause the escape sequence to be sent, however (such as by viewing a malicious text document with the "cat" command). Whether you [...] Solution : http://www.debian.org/security/2003/dsa-380 Network Security Threat Level: High Networks Security ID: 4396, 6940, 6950, 8514 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

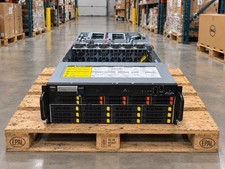
Gigabyte 4U AI Server 10x Nvidia GPU 2x Xeon Gold 6150 36 Core 2.7GHz DDR4 RAM
$1625.00

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00
867959-B21 HPE ProLiant DL360 G10 CTO Server W/ 2x 865414-B21 1x 840140-001
$245.00

Dell PowerEdge R240 Intel Xeon E-2224 3.50GHz 8GB DDR4 ECC NO HDD 250W
$285.97

Dell PowerEdge R730XD 28 Core Server 2X Xeon E5-2680 V4 H730 32GB RAM No HDD
$378.93
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2690 v3 | 64gb Ram | 2x 1600W
$524.99
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2680 v3 | 32gb Ram | 2x 1600W
$409.99
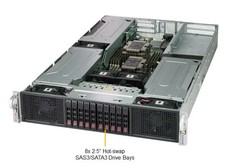
Supermicro 2U GPU Server SYS-2029GP-TR 2x Xeon 6130 32C 6x PCIe 3.0 x16 Slots
$745.00

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00

Dell PowerEdge R530 2x E5-2630v4 H330 iDRAC8 Port Card Riser No PSU/RAM/HDD
$99.99
|
||
|
No Discussions have been posted on this vulnerability. |