|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA379] DSA-379-1 sane-backends Vulnerability Assessment Details
|
[DSA379] DSA-379-1 sane-backends |
||
|
DSA-379-1 sane-backends Detailed Explanation for this Vulnerability Assessment Alexander Hvostov, Julien Blache and Aurelien Jarno discovered several security-related problems in the sane-backends package, which contains an API library for scanners including a scanning daemon (in the package libsane) that can be remotely exploited. These problems permit a remote attacker to cause a segmentation fault and/or consume arbitrary amounts of memory. The attack is successful, even if the attacker's computer isn't listed in saned.conf. You are only vulnerable if you actually run saned e.g. in xinetd or inetd. If the entries in the configuration file of xinetd or inetd respectively are commented out or do not exist, you are safe. Try "telnet localhost 6566" on the server that may run saned. If you get "connection refused" saned is not running and you are safe. The Common Vulnerabilities and Exposures project identifies the following problems: CVE-2003-0773: saned checks the identity (IP address) of the remote host only after the first communication took place (SANE_NET_INIT). So everyone can send that RPC, even if the remote host is not permited to scan (not listed in saned.conf). saned lacks error checking nearly everywhere in the code. So connection drops are detected very late. If the drop of the connection isn't detected, the access to the internal wire buffer leaves the limits of the allocated memory. So random memory "after" the wire buffer is read which will be followed by a segmentation fault. If saned expects strings, it mallocs the memory necessary to store the complete string after it receives the size of the string. If the connection was dropped before transmitting the size, malloc will reserve an arbitrary size of memory. Depending on that size and the amount of memory available either malloc fails (->saned quits nicely) or a huge amount of memory is allocated. Swapping and OOM measures may occur depending on the kernel. saned doesn't check the validity of the RPC numbers it gets before getting the parameters. If debug messages are enabled and a connection is dropped, non-null-terminated strings may be printed and segmentation faults may occur. It's possible to allocate an arbitrary amount of memory on the server running saned even if the connection isn't dropped. At the moment this cannot easily be fixed according to the author. Better limit the total amount of memory saned may use (ulimit). For the stable distribution (woody) this problem has been fixed in version 1.0.7-4. For the unstable distribution (sid) this problem has been fixed in version 1.0.11-1 and later. We recommend that you upgrade your libsane packages. Solution : http://www.debian.org/security/2003/dsa-379 Network Security Threat Level: High Networks Security ID: 8593, 8594, 8595, 8596, 8597, 8600 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

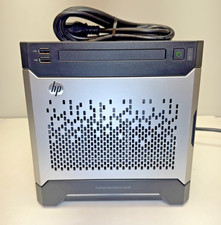
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
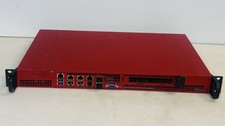
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
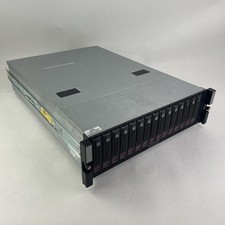
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
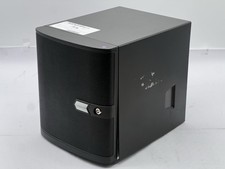
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
Supermicro 1027GR-TSF 1U Rackmount Server 2x Xeon 2.3GHz 128GB DDR3
$219.99
$280.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |