|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA297] DSA-297-1 snort Vulnerability Assessment Details
|
[DSA297] DSA-297-1 snort |
||
|
DSA-297-1 snort Detailed Explanation for this Vulnerability Assessment Two vulnerabilities have been discovered in Snort, a popular network intrusion detection system. Snort comes with modules and tests that perform a variety of functions such as protocol analysis. The following issues have been identified: For the stable distribution (woody) these problems have been fixed in version 1.8.4beta1-3.1. The old stable distribution (potato) is not affected by these problems since it doesn't contain the problematic code. For the unstable distribution (sid) these problems have been fixed in version 2.0.0-1. We recommend that you upgrade your snort package immediately. You are also advised to upgrade to the most recent version of Snort, since Snort, as any intrusion detection system, is rather useless if it is based on old and out-dated data and not kept up to date. Such installations would be unable to detect intrusions using modern methods. The current version of Snort is 2.0.0, while the version in the stable distribution (1.8) is quite old and the one in the old stable distribution is beyond hope. Since Debian does not update arbitrary packages in stable releases, even Snort is not going to see updates other than to fix security problems, you are advised to upgrade to the most recent version from third party sources. The Debian maintainer for Snort provides backported up-to-date packages for woody (stable) and potato (oldstable) for cases where you cannot upgrade your entire system. These packages are untested, though and only exist for the i386 architecture: deb http://people.debian.org/~ssmeenk/snort-stable-i386/ ./ deb-src http://people.debian.org/~ssmeenk/snort-stable-i386/ ./ deb http://people.debian.org/~ssmeenk/snort-oldstable-i386/ ./ deb-src http://people.debian.org/~ssmeenk/snort-oldstable-i386/ ./ Solution : http://www.debian.org/security/2003/dsa-297 Network Security Threat Level: High Networks Security ID: 6963, 7178 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
Lot of 5 Cisco 10G SFP+ 850nm 300m Transceiver Module P/N: SFP-10G-SR-10-2415-03
$15.00
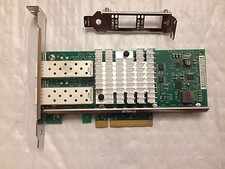
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
Lot of 10 ARISTA SFP-10G-SR 10GBASE-SR SFP LC Connector Optic Transceiver Module
$60.72
|
||
|
No Discussions have been posted on this vulnerability. |