|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA288] DSA-288-1 openssl Vulnerability Assessment Details
|
[DSA288] DSA-288-1 openssl |
||
|
DSA-288-1 openssl Detailed Explanation for this Vulnerability Assessment Researchers discovered two flaws in OpenSSL, a Secure Socket Layer (SSL) library and related cryptographic tools. Applications that are linked against this library are generally vulnerable to attacks that could leak the server's private key or make the encrypted session decryptable otherwise. The Common Vulnerabilities and Exposures (CVE) project identified the following vulnerabilities: For the stable distribution (woody) these problems have been fixed in version 0.9.6c-2.woody.3. For the old stable distribution (potato) these problems have been fixed in version 0.9.6c-0.potato.6. For the unstable distribution (sid) these problems have been fixed in version 0.9.7b-1 of openssl and version 0.9.6j-1 of openssl096. We recommend that you upgrade your openssl packages immediately and restart the applications that use OpenSSL. Unfortunately, RSA blinding is not thread-safe and will cause failures for programs that use threads and OpenSSL such as stunnel. However, since the proposed fix would change the binary interface (ABI), programs that are dynamically linked against OpenSSL won't run anymore. This is a dilemma we can't solve. You will have to decide whether you want the security update which is not thread-safe and recompile all applications that apparently fail after the upgrade, or fetch the additional source packages at the end of this advisory, recompile it and use a thread-safe OpenSSL library again, but also recompile all applications that make use of it (such as apache-ssl, mod_ssl, ssh etc.). However, since only very few packages use threads and link against the OpenSSL library most users will be able to use packages from this update without any problems. Solution : http://www.debian.org/security/2003/dsa-288 Network Security Threat Level: High Networks Security ID: 7101, 7148 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
Micron 16GB (2x8GB) 2Rx8 DDR3 1600MHz PC3-12800U Desktop RAM
$19.99
Crucial 32GB(4 x 8GB) CT8G4DFS824A.C8FDD1 DDR4-2400 UDIMM Desktop RAM - CR352A
$89.95
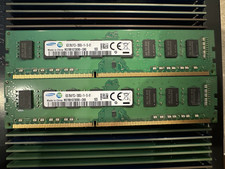
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
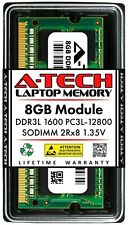
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
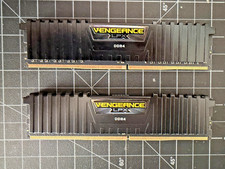
Corsair CMK16GX4M2Z3200C16 DDR4 16GB (2x8GB) 3200MHZ
$78.99
Dell 16GB PC4-21300 (DDR4-2666) Memory (SNPPWR5TC16G)
$89.99
|
||
|
No Discussions have been posted on this vulnerability. |