|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA269] DSA-269-1 heimdal Vulnerability Assessment Details
|
[DSA269] DSA-269-1 heimdal |
||
|
DSA-269-1 heimdal Detailed Explanation for this Vulnerability Assessment A cryptographic weakness in version 4 of the Kerberos protocol permits a possible hacker to use a chosen-plaintext attack to impersonate any principal in a realm. Additional cryptographic weaknesses in the krb4 implementation permit the use of cut-and-paste attacks to fabricate krb4 tickets for unauthorized client principals if triple-DES keys are used to key krb4 services. These attacks can subvert a site's entire Kerberos authentication infrastructure. This version of the heimdal package changes the default behavior and dispermits cross-realm authentication for Kerberos version 4. Because of the fundamental nature of the problem, cross-realm authentication in Kerberos version 4 cannot be made secure and sites should avoid its use. A new option (--kerberos4-cross-realm) is provided to the kdc command to re-enable version 4 cross-realm authentication for those sites that must use this functionality but desire the other security fixes. For the stable distribution (woody) this problem has been fixed in version 0.4e-7.woody.8. The old stable distribution (potato) is not affected by this problem, since it isn't compiled against kerberos 4. For the unstable distribution (sid) this problem has been fixed in version 0.5.2-1. We recommend that you upgrade your heimdal packages immediately. Solution : http://www.debian.org/security/2003/dsa-269 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

🔀 Juniper Networks EX2300-C-12P 12× Gigabit PoE+ • 2× 10G SFP+ Compact Switch ⚡
$109.99
Juniper EX2300 12-Port Gigabit PoE+ Managed Network Switch P/N: EX2300-C-12P
$149.99
Juniper EX3400-24P 24-Port PoE+ GbE + 4-Port 1/10Gb SFP Switch
$245.00
Juniper Networks Mist Wireless Access Points, Model AP45
$59.99
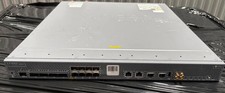
Juniper MX204 +JUNOS and Dual Power Supply
$7299.99
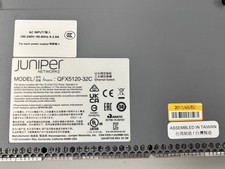
Juniper Networks QFX5120-32C Ethernet Switch, Server Component
$5999.95
Juniper Networks MX204-HW-BASE *BRAND NEW FACTORY SEALED* READ DETAILS
$8199.99
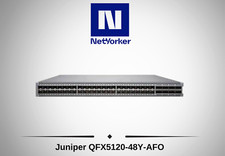
Juniper QFX5120-48Y-AFO 48 x 1/10/25GB SFP28 + 8 x 40/100GB Switch w/Dual AC
$10499.99
Juniper EX4300-24P 24 Port Gigabit PoE+ Switch.
$95.55
Juniper Networks EX3400-24T 24-Port Ethernet Switch w/Power Cord
$174.99
|
||
|
No Discussions have been posted on this vulnerability. |