|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA245] DSA-245-1 dhcp3 Vulnerability Assessment Details
|
[DSA245] DSA-245-1 dhcp3 |
||
|
DSA-245-1 dhcp3 Detailed Explanation for this Vulnerability Assessment Florian Lohoff discovered a bug in the dhcrelay causing it to send a continuing packet storm towards the configured DHCP server(s) in case of a malicious BOOTP packet, such as sent from buggy Cisco switches. When the dhcp-relay receives a BOOTP request it forwards the request to the DHCP server using the broadcast MAC address ff:ff:ff:ff:ff:ff which causes the network interface to reflect the packet back into the socket. To prevent loops the dhcrelay checks whether the relay-address is its own, in which case the packet would be dropped. In combination with a missing upper boundary for the hop counter an attacker can force the dhcp-relay to send a continuing packet storm towards the configured dhcp server(s). This patch introduces a new command line switch -c maxcount and people are advised to start the dhcp-relay with dhcrelay -c 10 or a smaller number, which will only create that many packets. The dhcrelay program from the "dhcp" package does not seem to be affected since DHCP packets are dropped if they were apparently relayed already. For the stable distribution (woody) this problem has been fixed in version 3.0+3.0.1rc9-2.2. The old stable distribution (potato) does not contain dhcp3 packages. For the unstable distribution (sid) this problem has been fixed in version 1.1.2-1. We recommend that you upgrade your dhcp3 package when you are using the dhcrelay server. Solution : http://www.debian.org/security/2003/dsa-245 Network Security Threat Level: High Networks Security ID: 6628 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Novell SUSE Linux Enterprise Server 9, Linux Professional 8.2 / 9.1 — 3 DVD Set
$58.00
Ubuntu Server 26.04.1 LTS Bootable USB Flash Drive – Latest September 2026
$12.99
OPNsense pfSense 8-Core Atom C3758 2.2GHz 8GB DDR4 64GB SSD 8x NIC QAT AES VPN
$125.00
RED HAT ENTERPRISE LINUX 5 SERVER RHF0382US-R1 for PC x86 AMD 64 INTEL 64 30 Day
$188.24
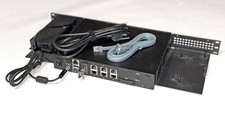
OPNsense Firewall VPN QAT 8-Core Atom C3758 2.20GHz 16GB DDR4 128GB SSD 8xNIC
$175.00
All New Ubuntu 26.04 LTS Linux Bootable USB Flash Drive
$15.95
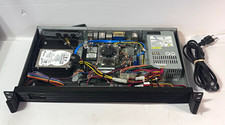
1U Rackmount PC Intel Core i5-2520M 8GB RAM 500GB HDD Ubuntu Linux Server
$109.99
ZimaBoard 2 1664 Home Server 16GB
$350.00
Microsoft SQL Server 2019 Enterprise 40 Core Unlimited CAL Retail License FPP
$299.00
SQL Server 2022 Enterprise 96 Core License & DVD Unlimited CALs with CoA
$284.99
|
||
|
No Discussions have been posted on this vulnerability. |