|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA237] DSA-237-1 kdenetwork Vulnerability Assessment Details
|
[DSA237] DSA-237-1 kdenetwork |
||
|
DSA-237-1 kdenetwork Detailed Explanation for this Vulnerability Assessment The KDE team discovered several vulnerabilities in the K Desktop Environment. In some instances KDE fails to properly quote parameters of instructions passed to a command shell for execution. These parameters may incorporate data such as URLs, filenames and e-mail addresses, and this data may be provided remotely to a victim in an e-mail, a webpage or files on a network filesystem or other untrusted source. By carefully crafting such data a possible hacker might be able to execute arbitrary commands on a vulnerable system using the victim's account and rights. The KDE Project is not aware of any existing exploits of these vulnerabilities. The patches also provide better safe guards and check data from untrusted sources more strictly in multiple places. For the current stable distribution (woody), these problems have been fixed in version 2.2.2-14.6. The old stable distribution (potato) does not contain KDE packages. For the unstable distribution (sid), these problems will most probably not be fixed but new packages for KDE 3.1 for sid are expected for this year. We recommend that you upgrade your KDE packages. Solution : http://www.debian.org/security/2003/dsa-237 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

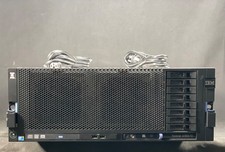
IBM System X3850-X5 Server w/4x Intel Xeon E7-4870 CPU , 512 GB DDR3 RAM,NO HDD
$1299.99
IBM ADP Server Type 7870 AC1 NO HDD | 128GB RAM PC3L | 2 x Xeon E5620
$199.99
Unused IBM 09P0037 MAINBOARD For RS/6000 7044-170 P-Series
$375.00
IBM QRadar xx29 2x Xeon E5-2650v4 2x 900W PSU M5120 12x 3.5" Bay Server No RAM
$179.99
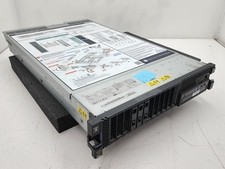
IBM Power 8 S822L Server 8247-22L POWER8 Enterprise 256GB RAM 2x 00KV626 CPU
$999.99
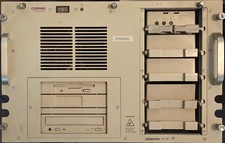
Compaq ProLiant 1500R 5/100 rack server, Series 3155, with IBM 2.1GB HD, VINTAGE
$295.00
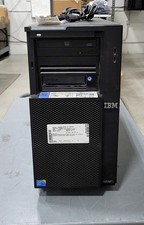
IBM SYSTEM X3500 M3 SERVER 7380AC1 TOWER Server XEON E5620 8GB RAID SEE NOTES
$110.30
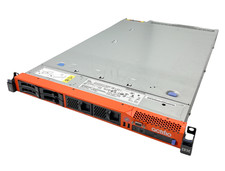
IBM System x3550 M3 1U Server 2x Xeon E5645, 192GB RAM, 2x 300GB HDD (7944-AC1)
$150.00
Rare Vintage IBM 93ZZ PowerPC Server Board - MCM Ceramic CPU - 40N1844 - 1.1 lbs
$49.99
DELL POWEREDGE HP IBM SERVER XEON GOLD 5315Y 8 CORE PROCESSOR 3.2 GHZ SRKXR
$1100.00
|
||
|
No Discussions have been posted on this vulnerability. |