|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA218] DSA-218-1 bugzilla Vulnerability Assessment Details
|
[DSA218] DSA-218-1 bugzilla |
||
|
DSA-218-1 bugzilla Detailed Explanation for this Vulnerability Assessment A cross site scripting vulnerability has been reported for Bugzilla, a web-based bug tracking system. Bugzilla does not properly sanitize any input submitted by users for use in quips. As a result, it is possible for a remote attacker to create a malicious link containing script code which will be executed in the browser of a legitimate user, in the context of the website running Bugzilla. This issue may be exploited to steal cookie-based authentication credentials from legitimate users of the website running the vulnerable software. This vulnerability only affects users who have the 'quips' feature enabled and who upgraded from version 2.10 which did not exist inside of Debian. The Debian package history of Bugzilla starts with 1.13 and jumped to 2.13. However, users could have installed version 2.10 prior to the Debian package. For the current stable distribution (woody) this problem has been fixed in version 2.14.2-0woody3. The old stable distribution (potato) does not contain a Bugzilla package. For the unstable distribution (sid) this problem will be fixed soon. We recommend that you upgrade your bugzilla packages. Solution : http://www.debian.org/security/2002/dsa-218 Network Security Threat Level: High Networks Security ID: 6257 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

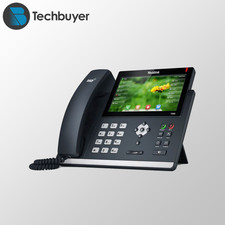
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
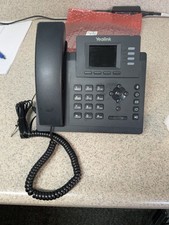
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
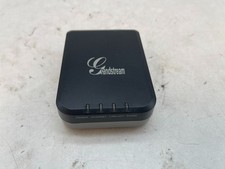
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
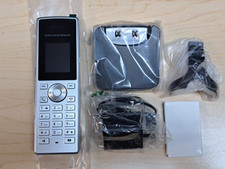
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28

Cisco / Linksys SPA2102 VoIP 2FXS Phone Adapter with Router (unlocked)
$18.99
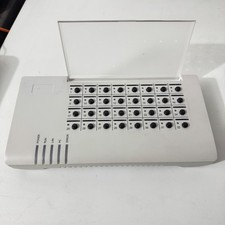
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
Poly CCX 400 Desktop Business Media Phone VoIP 2200-49700-019
$49.99
|
||
|
No Discussions have been posted on this vulnerability. |