|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA181] DSA-181-1 libapache-mod-ssl Vulnerability Assessment Details
|
[DSA181] DSA-181-1 libapache-mod-ssl |
||
|
DSA-181-1 libapache-mod-ssl Detailed Explanation for this Vulnerability Assessment Joe Orton discovered a cross site scripting problem in mod_ssl, an Apache module that adds Strong cryptography (i.e. HTTPS support) to the webserver. The module will return the server name unescaped in the response to an HTTP request on an SSL port. Like the other recent Apache XSS bugs, this only affects servers using a combination of "UseCanonicalName off" (default in the Debian package of Apache) and wildcard DNS. This is very unlikely to happen, though. Apache 2.0/mod_ssl is not vulnerable since it already escapes this HTML. With this setting turned on, whenever Apache needs to construct a self-referencing URL (a URL that refers back to the server the response is coming from) it will use ServerName and Port to form a "canonical" name. With this setting off, Apache will use the hostname:port that the client supplied, when possible. This also affects SERVER_NAME and SERVER_PORT in CGI scripts. This problem has been fixed in version 2.8.9-2.1 for the current stable distribution (woody), in version 2.4.10-1.3.9-1potato4 for the old stable distribution (potato) and version 2.8.9-2.3 for the unstable distribution (sid). We recommend that you upgrade your libapache-mod-ssl package. Solution : http://www.debian.org/security/2002/dsa-181 Network Security Threat Level: High Networks Security ID: 6029 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
Samsung 64GB PC4-2666V-R 2S2Rx4 DDR4 ECC REG RDIMM - M393A8K40B22-CWD6Y
$270.00
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
Lot 500 SK hynix 16GB 2Rx8 PC4-23400 DDR4-2933Y ECC Registered Server Memory RAM
$47988.00
Corsair Vengeance DDR3 8GB 16GB 32GB 1866MHz PC3-14900 Desktop RAM Memory DIMM
$85.00
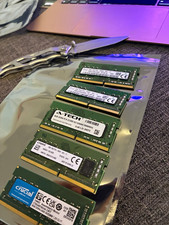
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
|
||
|
No Discussions have been posted on this vulnerability. |