|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA168] DSA-168-1 php Vulnerability Assessment Details
|
[DSA168] DSA-168-1 php |
||
|
DSA-168-1 php Detailed Explanation for this Vulnerability Assessment Wojciech Purczynski found out that it is possible for scripts to pass arbitrary text to sendmail as commandline extension when sending a mail through PHP even when safe_mode is turned on. Passing 5th argument should be disabled if PHP is configured in safe_mode, which is the case for newer PHP versions and for the versions below. This does not affect PHP3, though. Wojciech Purczynski also found out that arbitrary ASCII control characters may be injected into string arguments of the mail() function. If mail() arguments are taken from user's input it may give the user ability to alter message content including mail headers. Ulf H�rnhammar discovered that file() and fopen() are vulnerable to CRLF injection. A possible hacker could use it to escape certain restrictions and add arbitrary text to alleged HTTP requests that are passed through. However this only happens if something is passed to these functions which is neither a valid file name nor a valid url. Any string that contains control chars cannot be a valid url. Before you pass a string that should be a url to any function you must use urlencode() to encode it. Three problems have been identified in PHP: These problems have been fixed in version 3.0.18-23.1woody1 for PHP3 and 4.1.2-5 for PHP4 for the current stable distribution (woody), in version 3.0.18-0potato1.2 for PHP3 and 4.0.3pl1-0potato4 for PHP4 in the old stable distribution (potato) and in version 3.0.18-23.2 for PHP3 and 4.2.3-3 for PHP4 for the unstable distribution (sid). We recommend that you upgrade your PHP packages. Solution : http://www.debian.org/security/2002/dsa-168 Network Security Threat Level: High Networks Security ID: 5681 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

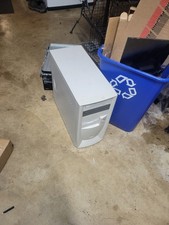
vintage pentium 3 pc turns on no display no post
$150.00
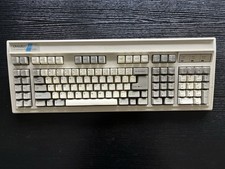
Vintage Computer Keyboard Northgate OMNIKEY Ultra
$120.00
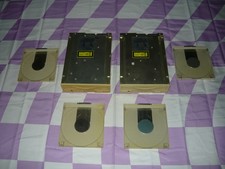
Lot of 2 Vintage Plextor PX-43CS SCSI CD-ROM Caddy Drives + 4 Caddies Used
$55.99
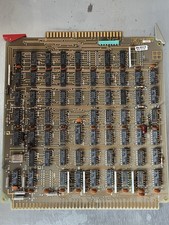
Vintage Hewlett Packard HP 13181-60074 Circuit Card Assembly / Interface Board.
$135.37
Vintage Avionics Gold CPU Board Intel MD8088 Ceramic LSI MCE Military Aerospace
$179.95
Vintage CREATIVE PC-DVD Dxr2 DVD2240E 1997
$59.00
Vintage Military Avionics PCB AlliedSignal 1750A CPU Ceramic Aerospace Board
$299.95
Vintage Military Avionics PCB Intel MG8097BH Ceramic CPU EPROM Circuit Board IC
$119.95
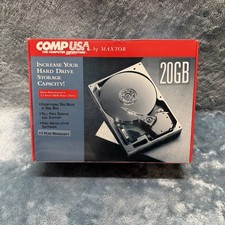
VINTAGE COLLECTIBLE Comp USA Maxtor 20 GB 3.5 Inch EIDE Hard Drive NEW SEALED
$500.00
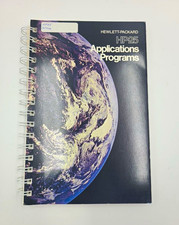
Vintage Hewlett-Packard HP-25 Applications Programs 1975 Manual 00025-90011
$29.50
|
||
|
No Discussions have been posted on this vulnerability. |