|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA163] DSA-163-1 mhonarc Vulnerability Assessment Details
|
[DSA163] DSA-163-1 mhonarc |
||
|
DSA-163-1 mhonarc Detailed Explanation for this Vulnerability Assessment Jason Molenda and Hiromitsu Takagi found ways to exploit cross site scripting bugs in mhonarc, a mail to HTML converter. When processing maliciously crafted mails of type text/html mhonarc does not deactivate all scripting parts properly. This is fixed in upstream version 2.5.3. If you are worried about security, it is recommended that you disable support of text/html messages in your mail archives. There is no guarantee that the mhtxthtml.pl library is robust enough to eliminate all possible exploits that can occur with HTML data. To exclude HTML data, you can use the MIMEEXCS resource. For example: text/html text/x-html The type "text/x-html" is probably not used any more, but is good to include it, just-in-case. If you are concerned that this could block out the entire contents of some messages, then you could do the following instead: text/html m2h_text_plain::filter mhtxtplain.pl text/x-html m2h_text_plain::filter mhtxtplain.pl This treats the HTML as text/plain. The above problems have been fixed in version 2.5.2-1.1 for the current stable distribution (woody), in version 2.4.4-1.1 for the old stable distribution (potato) and in version 2.5.11-1 for the unstable distribution (sid). We recommend that you upgrade your mhonarc packages. Solution : http://www.debian.org/security/2002/dsa-163 Network Security Threat Level: High Networks Security ID: 4546 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

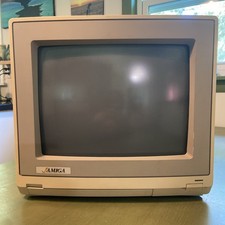
Amiga Model 1080 RGB color CRT monitor - Parts Or Repair - Doesn’t Power On
$100.00
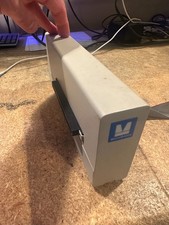
Microbotics Starboard 2MB + SCSI Sidecar for Amiga 1000 Vintage Computer READ
$329.00
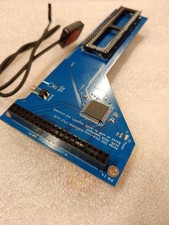
RGB2HDMI Amiga 500 UltraLong (Accelerator Friendly) HDMI Games, non-RTG A500
$50.00
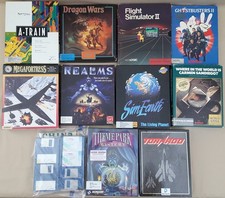
(10) BOXED Games for Commodore Amiga 500 600 1000 1200 2000 3000(T) 4000(T)
$329.98
Amiga Emplant Emulator Card For Commodore Amiga 2000 4000 3000
$249.00
Commodore Amiga 4000 Motherboard Rev B - untested
$225.00
HighFlyer Amiga 4000 Tower & Bus Extender, Expansion Systems A4000T Kit
$888.50
Commodore Amiga 1010 3.5" Floppy Disk Drive 880K WORKS GREAT
$179.00
Best FlickerFixer RGB2HDMI Amiga HDMI Games, non-RTG A2000CPLDSlot v2.2
$75.00
OPEN BOX - AMIGA Genlock Interface Vintage Video Adapter 1300- GREAT
$329.95
|
||
|
No Discussions have been posted on this vulnerability. |