|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA158] DSA-158-1 gaim Vulnerability Assessment Details
|
[DSA158] DSA-158-1 gaim |
||
|
DSA-158-1 gaim Detailed Explanation for this Vulnerability Assessment The developers of Gaim, an instant messenger client that combines several different networks, found a vulnerability in the hyperlink handling code. The 'Manual' browser command passes an untrusted string to the shell without escaping or reliable quoting, permitting a possible hacker to execute arbitrary commands on the users machine. Unfortunately, Gaim doesn't display the hyperlink before the user clicks on it. Users who use other inbuilt browser commands aren't vulnerable. This problem has been fixed in version 0.58-2.2 for the current stable distribution (woody) and in version 0.59.1-2 for the unstable distribution (sid). The old stable distribution (potato) is not affected since it doesn't ship the Gaim program. The fixed version of Gaim no longer passes the user's manual browser command to the shell. Commands which contain the %s in quotes will need to be amended, so they don't contain any quotes. The 'Manual' browser command can be edited in the 'General' pane of the 'Preferences' dialog, which can be accessed by clicking 'Options' from the login window, or 'Tools' and then 'Preferences' from the menu bar in the buddy list window. We recommend that you upgrade your gaim package immediately. Solution : http://www.debian.org/security/2002/dsa-158 Network Security Threat Level: High Networks Security ID: 5574 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |


Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$379.00

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$60.00
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99

Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
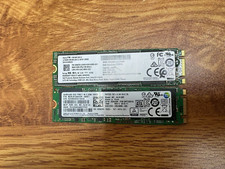
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
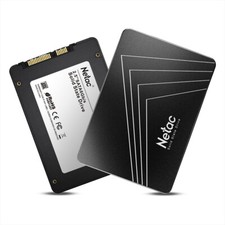
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99

Netac 256GB SSD 2.5'' SATA III 6Gb/s Internal Solid State Drive 500MB/s PC/Latop
$40.00
|
||
|
No Discussions have been posted on this vulnerability. |