|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA136] DSA-136-1 openssl Vulnerability Assessment Details
|
[DSA136] DSA-136-1 openssl |
||
|
DSA-136-1 openssl Detailed Explanation for this Vulnerability Assessment The OpenSSL development team has announced that a security audit by A.L. Digital Ltd and The Bunker, under the DARPA CHATS program, has revealed remotely exploitable buffer overflow conditions in the OpenSSL code. Additionally, the ASN1 parser in OpenSSL has a potential DoS attack independently discovered by Adi Stav and James Yonan. CVE-2002-0655 references overflows in buffers used to hold ASCII representations of integers on 64 bit platforms. CVE-2002-0656 references buffer overflows in the SSL2 server implementation (by sending an invalid key to the server) and the SSL3 client implementation (by sending a large session id to the client). The SSL2 issue was also noticed by Neohapsis, who have privately demonstrated exploit code for this issue. CVE-2002-0659 references the ASN1 parser DoS issue. These vulnerabilities have been addressed for Debian 3.0 (woody) in openssl094_0.9.4-6.woody.2, openssl095_0.9.5a-6.woody.1 and openssl_0.9.6c-2.woody.1. These vulnerabilities are also present in Debian 2.2 (potato). Fixed packages are available in openssl094_0.9.4-6.potato.2 and openssl_0.9.6c-0.potato.4. A worm is actively exploiting this issue on internet-attached hosts we recommend you upgrade your OpenSSL as soon as possible. Note that you must restart any daemons using SSL. (E.g., ssh or ssl-enabled apache.) If you are uncertain which programs are using SSL you may choose to reboot to ensure that all running daemons are using the new libraries. Solution : http://www.debian.org/security/2002/dsa-136 Network Security Threat Level: High Networks Security ID: 5353, 5361, 5362, 5363, 5364, 5366 Vulnerability Assessment Copyright: This script is (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

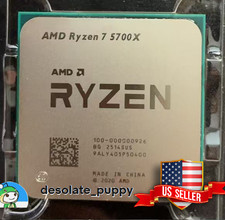
(New) AMD Ryzen 7 5700X 8 Core 16 Thread AM4 Unlocked 3.4 GHz CPU OEM Tray
$174.99
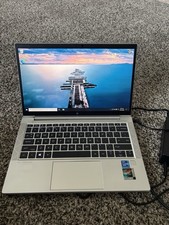
HP EliteBook 830 G8 Core I7-1185G7 3.00GHz Laptop 32GB RAM, 512GB SSD
$250.00
SGIN 17.3" Laptop Intel Quad-Core Up to 2.4 GHZ 8GB RAM 256GB SSD HD
$229.99
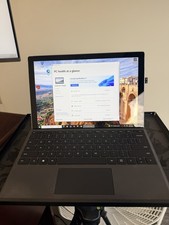
Microsoft Surface Pro 5 Silver 128GB SSD 4gb RAM
$97.97
Apple Macbook Pro 13" M1 8-Core 16GB 512GB - Good
$464.99
Intel Xeon E5 - 2667V2 / SR19W 3.30GHz 25MB 8-Core CPU Socket LGA2011
$30.00

AMD FX 8350 8-CORE 4.00GHz CPU FD8350FRW8KHK SOCKET AM3+ *QTY
$39.99
AMD Ryzen 7 9700X 8-Core 16-Thread 40MB Cache Socket AM5 9000 Series Processor
$245.99
Intel Core i7-11700T 1.4GHz Processor 8-Core Socket LGA1200 SRKNT
$129.95
Dell T7810 Workstation 8-Core 2.40GHz E5-2630 v3 No RAM GPU HDD OS
$259.98
|
||
|
No Discussions have been posted on this vulnerability. |