|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA1237] DSA-1237-1 kernel-source-2.4.27 Vulnerability Assessment Details
|
[DSA1237] DSA-1237-1 kernel-source-2.4.27 |
||
|
DSA-1237-1 kernel-source-2.4.27 Detailed Explanation for this Vulnerability Assessment Several local and remote vulnerabilities have been discovered in the Linux kernel that may lead to a denial of service or the execution of arbitrary code. The Common Vulnerabilities and Exposures project identifies the following problems: Olof Johansson reported a local DoS (Denial of Service) vulnerability on the PPC970 platform. Unpriveleged users can hang the system by executing the "attn" instruction, which was not being disabled at boot. Kirill Korotaev reported a local DoS (Denial of Service) vulnerability on the ia64 and sparc architectures. A user could cause the system to crash by executing a malformed ELF binary due to insufficient verification of the memory layout. ADLab Venustech Info Ltd reported a potential remote DoS (Denial of Service) vulnerability in the IP over ATM subsystem. A remote system could cause the system to crash by sending specially crafted packets that would trigger an attempt to free an already-freed pointer resulting in a system crash. Martin Schwidefsky reported a potential leak of sensitive information on s390 systems. The copy_from_user function did not clear the remaining bytes of the kernel buffer after receiving a fault on the userspace address, resulting in a leak of uninitialized kernel memory. A local user could exploit this by appending to a file from a bad address. Fabio Massimo Di Nitto reported a potential remote DoS (Denial of Service) vulnerability on powerpc systems. The alignment exception only checked the exception table for -EFAULT, not for other errors. This can be exploited by a local user to cause a system crash (panic). Bill Allombert reported that various mount options are ignored by smbfs when UNIX extensions are enabled. This includes the uid, gid and mode options. Client systems would silently use the server-provided settings instead of honoring these options, changing the security model. This update includes a fix from Haroldo Gamal that forces the kernel to honor these mount options. Note that, since the current versions of smbmount always pass values for these options to the kernel, it is not currently possible to activate unix extensions by omitting mount options. However, this behavior is currently consistent with the current behavior of the next Debian release, 'etch'. The following matrix explains which kernel version for which architecture fix the problems mentioned above: The following matrix lists additional packages that were rebuilt for compatibility with or to take advantage of this update: We recommend that you upgrade your kernel package immediately and reboot the machine. If you have built a custom kernel from the kernel source package, you will need to rebuild to take advantage of these fixes. Solution : http://www.debian.org/security/2006/dsa-1237 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

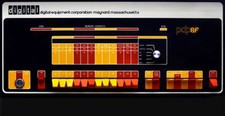
Computer Photo History Altair 8800 Philco 212 CDC 6600 DEC PDP-8 Apple 1 UNIVAC
$69.99
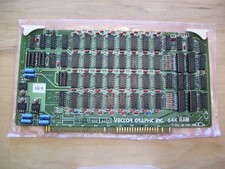
S-100 Vector Graphic 64K Ram Board (Altair, IMSAI)
$99.95
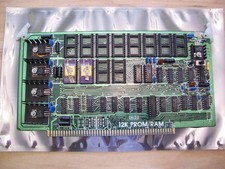
S-100 Vector Graphic 12K PROM/RAM Board (Altair, IMSAI)
$99.95
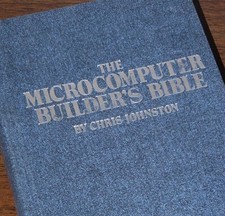
Microcomputer Builder's Bible IMSAI 8080 Z80 ADM-3A DEC LSI-11 Altair 8800 Bus
$65.00
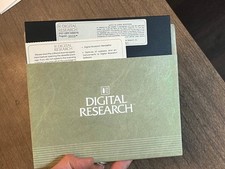
Vintage Digital Research ZSID 1.4 8" Floppy Disk CP/M Z80 Software S-100 Altair
$69.99
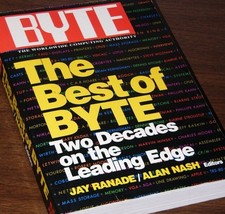
640pg Best of BYTE Magazine 1984 Mac Steve Jobs Altair 8800 IBM 5100 Bob Moog
$85.00
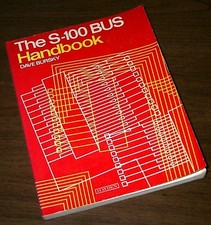
S-100 Bus Handbook Altair 8800 IMSAI 8080 Board Schematics Xitan Pertec Cromemco
$89.99
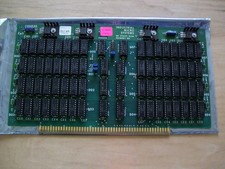
S-100 Industrial Micro Systems 8K Static Ram (IMS, Altair, IMSAI)
$69.95
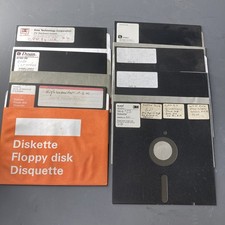
CP/M 86 1.1R 8086 Highmonitor 8 Inch Floppy Diskette 80s IMSAI Altair
$29.99
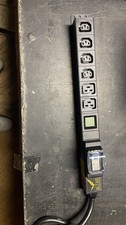
ALTAIR Bitcoin Mining Solutions PDU IEC SERIES 100-250V 30A/24A Power Distribute
$99.00
|
||
|
No Discussions have been posted on this vulnerability. |