|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA1233] DSA-1233-1 kernel-source-2.6.8 Vulnerability Assessment Details
|
[DSA1233] DSA-1233-1 kernel-source-2.6.8 |
||
|
DSA-1233-1 kernel-source-2.6.8 Detailed Explanation for this Vulnerability Assessment Several local and remote vulnerabilities have been discovered in the Linux kernel that may lead to a denial of service or the execution of arbitrary code. The Common Vulnerabilities and Exposures project identifies the following problems: Stephane Eranian discovered a local DoS (Denial of Service) vulnerability on the ia64 architecture. A local user could exhaust the available file descriptors by exploiting a counting error in the permonctl() system call. Kirill Korotaev reported a local DoS (Denial of Service) vulnerability on the ia64 and sparc architectures. A user could cause the system to crash by executing a malformed ELF binary due to insufficient verification of the memory layout. Dmitriy Monakhov reported a potential memory leak in the __block_prepare_write function. __block_prepare_write does not properly sanitize kernel buffers during error recovery, which could be exploited by local users to gain access to sensitive kernel memory. ADLab Venustech Info Ltd reported a potential remote DoS (Denial of Service) vulnerability in the IP over ATM subsystem. A remote system could cause the system to crash by sending specially crafted packets that would trigger an attempt to free an already-freed pointer resulting in a system crash. Martin Schwidefsky reported a potential leak of sensitive information on s390 systems. The copy_from_user function did not clear the remaining bytes of the kernel buffer after receiving a fault on the userspace address, resulting in a leak of uninitialized kernel memory. A local user could exploit this by appending to a file from a bad address. James Morris reported a potential local DoS (Denial of Service) vulnerability that could be used to hang or oops a system. The seqfile handling for /proc/net/ip6_flowlabel has a flaw that can be exploited to cause an infinite loop by reading this file after creating a flowlabel. Fabio Massimo Di Nitto reported a potential remote DoS (Denial of Service) vulnerability on powerpc systems. The alignment exception only checked the exception table for -EFAULT, not for other errors. This can be exploited by a local user to cause a system crash (panic). Eugene Teo reported a vulnerability in the get_fdb_entries function that could potentially be exploited to permit arbitrary code execution with escalated rights. Bill Allombert reported that various mount options are ignored by smbfs when UNIX extensions are enabled. This includes the uid, gid and mode options. Client systems would silently use the server-provided settings instead of honoring these options, changing the security model. This update includes a fix from Haroldo Gamal that forces the kernel to honor these mount options. Note that, since the current versions of smbmount always pass values for these options to the kernel, it is not currently possible to activate unix extensions by omitting mount options. However, this behavior is currently consistent with [...] Solution : http://www.debian.org/security/2006/dsa-1233 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

GIGABYTE A520M DS3H AC AMD AM4 Motherboard mATX
$59.99
GIGABYTE Z790 AORUS ELITE AX LGA 1700 Intel Z790 ATX Motherboard with DDR5
$189.99
Intel H310 LGA1151 8-9th Gen DDR4 M.2 NVMe mATX Motherboard IO Shield Battery
$54.99
ASUS PRIME Z490-V Motherboard Intel Z490 10th gen DDR4 LGA 1200 ATX w/ IO Shield
$84.99
GIGABYTE B365 HD3 LGA1151 Intel 9th Gen motherboard
$59.99
Intel H81 Motherboard M.2 NVMe LGA 1150 mATX w/ IO Shield (Random Slot Color)
$29.90
ASUS PRIME B360M-C MicroATX Intel LGA1151 DDR4 HDMI VGA USB RJ-45 Audio
$34.99
ASUS TUF GAMING B550-PLUS WIFI II AM4 AMD B550 ATX AMD Motherboard
$95.99
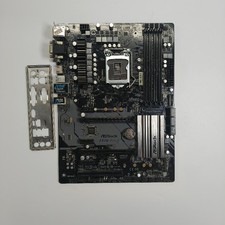
ASRock Z370 Pro4 LGA 1151 Z370 HDMI USB 3.1 2 Ultra M.2 DDR4 ATX Motherboard
$75.00
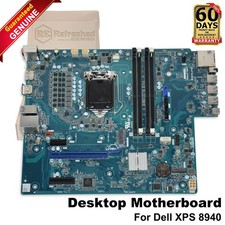
Dell XPS 8940 Desktop Motherboard Intel H470 LGA1200 DDR4 K3CM7 KV3RP 427JK
$154.99
|
||
|
No Discussions have been posted on this vulnerability. |