|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA1225] DSA-1225-2 mozilla-firefox Vulnerability Assessment Details
|
[DSA1225] DSA-1225-2 mozilla-firefox |
||
|
DSA-1225-2 mozilla-firefox Detailed Explanation for this Vulnerability Assessment This update covers packages for the little endian MIPS architecture missing in the original advisory. For reference please find below the original advisory text: Several security related problems have been discovered in Mozilla and derived products such as Mozilla Firefox. The Common Vulnerabilities and Exposures project identifies the following vulnerabilities: Tomas Kempinsky discovered that malformed FTP server responses could lead to denial of service. Ulrich K�hn discovered that the correction for a cryptographic flaw in the handling of PKCS-1 certificates was incomplete, which permits the forgery of certificates. "shutdown" discovered that modification of JavaScript objects during execution could lead to the execution of arbitrary JavaScript bytecode. Jesse Ruderman and Martijn Wargers discovered several crashes in the layout engine, which might also permit execution of arbitrary code. Igor Bukanov and Jesse Ruderman discovered several crashes in the JavaScript engine, which might permit execution of arbitrary code. This update also addresses several crashes, which could be triggered by malicious websites and fixes a regression introduced in the previous Mozilla update. For the stable distribution (sarge) these problems have been fixed in version 1.0.4-2sarge13. For the unstable distribution (sid) these problems have been fixed in the current iceweasel package 2.0+dfsg-1. We recommend that you upgrade your mozilla-firefox package. Solution : http://www.debian.org/security/2006/dsa-1225 Network Security Threat Level: High Networks Security ID: 19678, 20957 Vulnerability Assessment Copyright: This script is (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

RAM-HOL-SAM60CPU RAM USB-C Powered Dock for Samsung Tab Active5 - 3 - 2
$81.99

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
Samsung Galaxy Tab A9+ Plus 11” 128GB Android Tablet Graphite BRAND NEW SEALED.
$214.99

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
RAM-GDS-SKIN-SAM54-NG-1 RAM Mounts IntelliSkin® Next Gen for Samsung Tab Active4
$93.99
RAM-HOL-SAM52CPU RAM USB-C Powered Dock Samsung Tab Active4 Pro & Tab Active Pro
$81.99
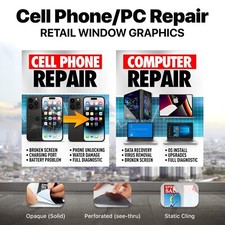
Cell Phone Smartphone Computer repair banner poster sign iphone Samsung
$89.99
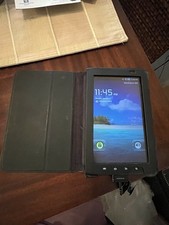
Samsung Galaxy Tab SCH-1800 7" 4GB Wi-Fi + Verizon Tablet Working
$30.00
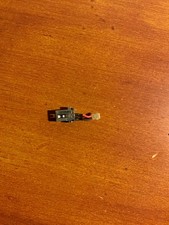
Samsung Galaxy View Tablet 18.4 SM-T670/677A Charging Port 100% Original Oem
$98.99
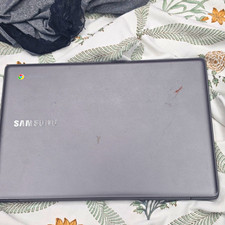
Samsung Chromebook 11.6" Intel Celeron Chrome OS Gray (Charger Inc)
$22.00
|
||
|
No Discussions have been posted on this vulnerability. |