|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA122] DSA-122-1 zlib Vulnerability Assessment Details
|
[DSA122] DSA-122-1 zlib |
||
|
DSA-122-1 zlib Detailed Explanation for this Vulnerability Assessment The compression library zlib has a flaw in which it attempts to free memory more than once under certain conditions. This can possibly be exploited to run arbitrary code in a program that includes zlib. If a network application running as root is linked to zlib, this could potentially lead to a remote root compromise. No exploits are known at this time. This vulnerability is assigned the CVE candidate name of CVE-2002-0059. The zlib vulnerability is fixed in the Debian zlib package version 1.1.3-5.1. A number of programs either link statically to zlib or include a private copy of zlib code. These programs must also be upgraded to eliminate the zlib vulnerability. The affected packages and fixed versions follow: Those using the pre-release (testing) version of Debian should upgrade to zlib 1.1.3-19.1 or a later version. Note that since this version of Debian has not yet been released it may not be available immediately for all architectures. Debian 2.2 (potato) is the latest supported release. We recommend that you upgrade your packages immediately. Note that you should restart all programs that use the shared zlib library in order for the fix to take effect. This is most easily done by rebooting the system. Solution : http://www.debian.org/security/2002/dsa-122 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$19.99
Cisco Catalyst 2960-48TT-L 48-Port Fast Ethernet Managed Rackmount Switch
$46.99
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$49.99
TP-Link TL-SG1048 48-Port Gigabit Rackmount Switch New Factory Sealed
$199.99
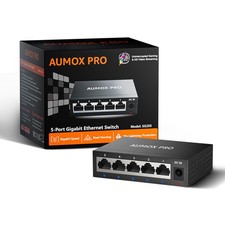
5 Port Gigabit Unmanaged Ethernet Switch, Home Network Hub, Office Ethernet S...
$9.64
10-Port Gigabit PoE Network Switch with 8 PoE+ Ports with 2 Combo SFP Slots 125W
$39.99
Arista DCS-7010T-48-R 48P 1GbE 4P 10GbE SFP+ RA Switch with rack mounts
$69.00
TP-Link TL-SG2210P 10-Port Gigabit Smart Switch w/ 8-Port PoE+ NO AC SKU 25597
$36.98
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$25.99
Linksys LGS328MPC 24-Port Managed Gigabit PoE+ Switch with 4 10G SFP+ Uplinks
$224.95
|
||
|
No Discussions have been posted on this vulnerability. |