|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA1189] DSA-1189-1 openssh-krb5 Vulnerability Assessment Details
|
[DSA1189] DSA-1189-1 openssh-krb5 |
||
|
DSA-1189-1 openssh-krb5 Detailed Explanation for this Vulnerability Assessment Several remote vulnerabilities have been discovered in OpenSSH, a free implementation of the Secure Shell protocol, which may lead to denial of service and potentially the execution of arbitrary code. The Common Vulnerabilities and Exposures project identifies the following problems: Tavis Ormandy of the Google Security Team discovered a denial of service vulnerability in the mitigation code against complexity attacks, which might lead to increased CPU consumption until a timeout is triggered. This is only exploitable if support for SSH protocol version 1 is enabled. Mark Dowd discovered that insecure signal handler usage could potentially lead to execution of arbitrary code through a double free. The Debian Security Team doesn't believe the general openssh package without Kerberos support to be exploitable by this issue. However, due to the complexity of the underlying code we will issue an update to rule out all eventualities. For the stable distribution (sarge) these problems have been fixed in version 3.8.1p1-7sarge1. For the unstable distribution (sid) these problems have been fixed in version 4.3p2-4 of openssh. openssh-krb5 will soon be converted towards a transitional package against openssh. We recommend that you upgrade your openssh-krb5 packages. Solution : http://www.debian.org/security/2006/dsa-1189 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2007 Michel Arboi |
||
|
Cables, Connectors |


Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$60.00

Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$1090.00
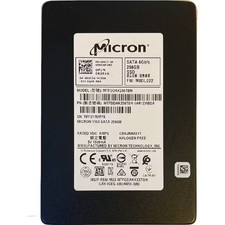
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00
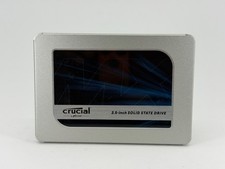
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
Fanxiang 256GB 512GB 1TB 2TB 4TB SSD Lot 2.5'' SATA Internal Solid State Drive
$42.99
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99
|
||
|
No Discussions have been posted on this vulnerability. |