|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA1161] DSA-1161-2 mozilla-firefox Vulnerability Assessment Details
|
[DSA1161] DSA-1161-2 mozilla-firefox |
||
|
DSA-1161-2 mozilla-firefox Detailed Explanation for this Vulnerability Assessment The latest security updates of Mozilla Firefox introduced a regression that led to a disfunctional attachment panel which warrants a correction to fix this issue. For reference please find below the original advisory text: Several security related problems have been discovered in Mozilla and derived products like Mozilla Firefox. The Common Vulnerabilities and Exposures project identifies the following vulnerabilities: The Javascript engine might permit remote attackers to execute arbitrary code. [MFSA-2006-50] Multiple integer overflows in the Javascript engine might permit remote attackers to execute arbitrary code. [MFSA-2006-50] Specially crafted Javascript permits remote attackers to execute arbitrary code. [MFSA-2006-51] Remote Proxy AutoConfig (PAC) servers could execute code with elevated rights via a specially crafted PAC script. [MFSA-2006-52] Scripts with the UniversalBrowserRead privilege could gain UniversalXPConnect rights and possibly execute code or obtain sensitive data. [MFSA-2006-53] Multiple vulnerabilities permit remote attackers to cause a denial of service (crash) and possibly execute arbitrary code. [MFSA-2006-55] For the stable distribution (sarge) these problems have been fixed in version 1.0.4-2sarge11. For the unstable distribution (sid) these problems have been fixed in version 1.5.dfsg+1.5.0.5-1. We recommend that you upgrade your mozilla-firefox package. Solution : http://www.debian.org/security/2006/dsa-1161 Network Security Threat Level: High Networks Security ID: 19181 Vulnerability Assessment Copyright: This script is (C) 2007 Michel Arboi |
||
|
Cables, Connectors |


Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99

Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$1090.00
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
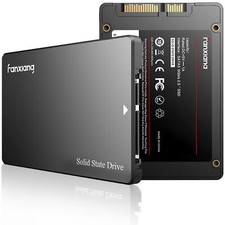
Fanxiang 256GB 512GB 1TB 2TB 4TB SSD Lot 2.5'' SATA Internal Solid State Drive
$42.99
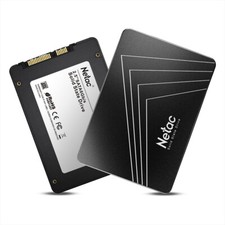
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99
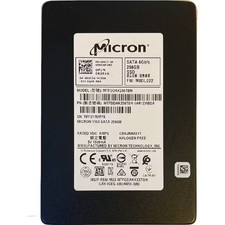
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00
|
||
|
No Discussions have been posted on this vulnerability. |