|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA1104] DSA-1104-2 openoffice.org Vulnerability Assessment Details
|
[DSA1104] DSA-1104-2 openoffice.org |
||
|
DSA-1104-2 openoffice.org Detailed Explanation for this Vulnerability Assessment Loading malformed XML documents can cause buffer overflows in OpenOffice.org, a free office suite, and cause a denial of service or execute arbitrary code. �It turned out that the correction in DSA 1104-1 was not sufficient, hence, another update. For completeness please find the original advisory text below: Several vulnerabilities have been discovered in OpenOffice.org, a free office suite. The Common Vulnerabilities and Exposures Project identifies the following problems: It turned out to be possible to embed arbitrary BASIC macros in documents in a way that OpenOffice.org does not see them but executes them anyway without any user interaction. It is possible to evade the Java sandbox with specially crafted Java applets. Loading malformed XML documents can cause buffer overflows and cause a denial of service or execute arbitrary code. This update has the Mozilla component disabled, so that the Mozilla/LDAP addressbook feature won't work anymore. It didn't work on anything else than i386 on sarge either. The old stable distribution (woody) does not contain OpenOffice.org packages. For the stable distribution (sarge) this problem has been fixed in version 1.1.3-9sarge3. For the unstable distribution (sid) this problem has been fixed in version 2.0.3-1. We recommend that you upgrade your OpenOffice.org packages. Solution : http://www.debian.org/security/2006/dsa-1104 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
Supermicro 1027GR-TSF 1U Rackmount Server 2x Xeon 2.3GHz 128GB DDR3
$219.99
$280.00
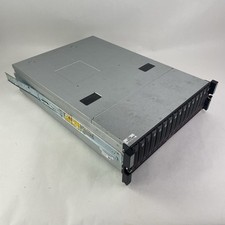
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |