|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA1097] DSA-1097-1 kernel-source-2.4.27 Vulnerability Assessment Details
|
[DSA1097] DSA-1097-1 kernel-source-2.4.27 |
||
|
DSA-1097-1 kernel-source-2.4.27 Detailed Explanation for this Vulnerability Assessment Several local and remote vulnerabilities have been discovered in the Linux kernel that may lead to a denial of service or the execution of arbitrary code. The Common Vulnerabilities and Exposures project identifies the following problems: "Solar Designer" discovered that arithmetic computations in netfilter's do_replace() function can lead to a buffer overflow and the execution of arbitrary code. However, the operation requires CAP_NET_ADMIN rights, which is only an issue in virtualization systems or fine grained access control systems. "Solar Designer" discovered a race condition in netfilter's do_add_counters() function, which permits information disclosure of kernel memory by exploiting a race condition. Like CVE-2006-0038, it requires CAP_NET_ADMIN rights. Intel EM64T systems were discovered to be susceptible to a local DoS due to an endless recursive fault related to a bad ELF entry address. Incorrectly declared die_if_kernel() function as "does never return" which could be exploited by a local attacker resulting in a kernel crash. AMD64 machines (and other 7th and 8th generation AuthenticAMD processors) were found to be vulnerable to sensitive information leakage, due to how they handle saving and restoring the FOP, FIP, and FDP x87 registers in FXSAVE/FXRSTOR when an exception is pending. This permits a process to acertain portions of the state of floating point instructions of other processes. Marco Ivaldi discovered that there was an unintended information disclosure permiting remote attackers to bypass protections against Idle Scans (nmap -sI) by abusing the ID field of IP packets and bypassing the zero IP ID in DF packet countermeasure. This was a result of the ip_push_pending_frames function improperly incremented the IP ID field when sending a RST after receiving unsolicited TCP SYN-ACK packets. Pavel Kankovsky reported the existence of a potential information leak resulting from the failure to initialize sin.sin_zero in the IPv4 socket code. Shaun Tancheff discovered a buffer overflow (boundary condition error) in the USB Gadget RNDIS implementation permiting remote attackers to cause a DoS. While creating a reply message, the driver allocated memory for the reply data, but not for the reply structure. The kernel fails to properly bounds-check user-supplied data before copying it to an insufficiently sized memory buffer. Attackers could crash the system, or possibly execute arbitrary machine code. Hugh Dickins discovered an issue in the madvise_remove() function wherein file and mmap restrictions are not followed, permiting local users to bypass IPC permissions and replace portions of readonly tmpfs files with zeroes. Alexandra Kossovsky reported a NULL pointer dereference condition in ip_route_input() that can be triggered by a local user by requesting a route for a multicast IP address, resulting in a denial of service (panic). Vlad [...] Solution : http://www.debian.org/security/2006/dsa-1097 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

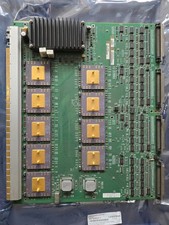
Vintage DEC E2052-AA AlphaServer I/O Board 9 Gold Ceramic ICs 4.3 LB Gold Scrap
$729.99
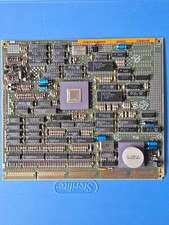
Vintage DEC Digital T1043 DWMBB/B VAXBI XMI Adapter 5018232-01 C1 VAX Board
$109.99
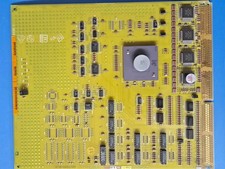
Vintage DEC Digital XMI-A1 5017293-01A1 LWPR BE3-0 VAX Circuit Board T2012
$74.99
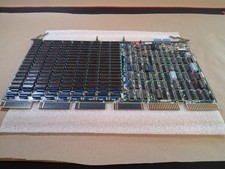
Vintage DEC/Mostek memory systems MK 8015 AA-00 6805-08015 1100 REV C(B7)
$279.99
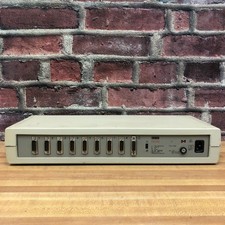
Vintage DEC Digital Equipment DELNI 8-Port Ethernet Local Network Hub VAXstation
$79.95
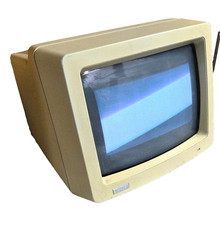
Vintage Digital VR241-A color CRT monitor, powers on, DEC Rainbow or terminal
$150.00
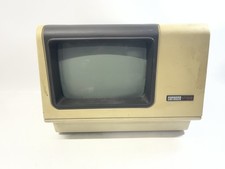
Vintage DEC VT100 Series Terminal (Powers On)
$499.99
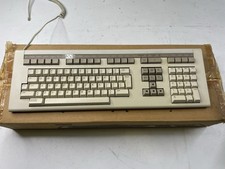
Vintage DEC LK201 Digital Equipment Corporation (DEC) LK201-AA Computer Keyboard
$149.99
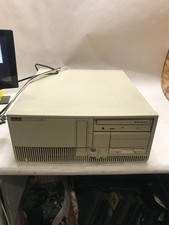
Vintage DEC Digital Starion 200 Desktop PC Powers On Boots To BIOS NO HDD - DW
$269.99
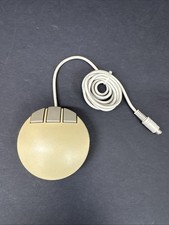
Vintage DEC Digital VSXXX-AA.B03 Hawley 3-Button Mouse 1986 Tested Working
$111.00
|
||
|
No Discussions have been posted on this vulnerability. |