|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA1051] DSA-1051-1 mozilla-thunderbird Vulnerability Assessment Details
|
[DSA1051] DSA-1051-1 mozilla-thunderbird |
||
|
DSA-1051-1 mozilla-thunderbird Detailed Explanation for this Vulnerability Assessment Several security related problems have been discovered in Mozilla Thunderbird. The Common Vulnerabilities and Exposures project identifies the following vulnerabilities: The "run-mozilla.sh" script permits local users to create or overwrite arbitrary files when debugging is enabled via a symlink attack on temporary files. Web pages with extremely long titles cause subsequent launches of the browser to appear to "hang" for up to a few minutes, or even crash if the computer has insufficient memory. [MFSA-2006-03] The JavaScript interpreter does not properly dereference objects, which permits remote attackers to cause a denial of service or execute arbitrary code. [MFSA-2006-01] The function allocation code permits attackers to cause a denial of service and possibly execute arbitrary code. [MFSA-2006-01] XULDocument.persist() did not validate the attribute name, permiting a possible hacker to inject arbitrary XML and JavaScript code into localstore.rdf that would be read and acted upon during startup. [MFSA-2006-05] An anonymous researcher for TippingPoint and the Zero Day Initiative reported that an invalid and nonsensical ordering of table-related tags can be exploited to execute arbitrary code. [MFSA-2006-27] A particular sequence of HTML tags can cause memory corruption that can be exploited to execute arbitrary code. [MFSA-2006-18] Georgi Guninski reports that forwarding mail in-line while using the default HTML "rich mail" editor will execute JavaScript embedded in the e-mail message with full rights of the client. [MFSA-2006-21] The HTML rendering engine does not properly block external images from inline HTML attachments when "Block loading of remote images in mail messages" is enabled, which could permit remote attackers to obtain sensitive information. [MFSA-2006-26] A vulnerability potentially permits remote attackers to cause a denial of service and possibly execute arbitrary code. [MFSA-2006-20] A vulnerability potentially permits remote attackers to cause a denial of service and possibly execute arbitrary code. [MFSA-2006-20] A vulnerability potentially permits remote attackers to cause a denial of service and possibly execute arbitrary code. [MFSA-2006-20] A vulnerability potentially permits remote attackers to cause a denial of service and possibly execute arbitrary code. [MFSA-2006-20] A vulnerability potentially permits remote attackers to cause a denial of service and possibly execute arbitrary code. [MFSA-2006-20] Georgi Guninski reported two variants of using scripts in an XBL control to gain chrome rights when the page is viewed under "Print Preview". [MFSA-2006-25] "shutdown" discovered that the crypto.generateCRMFRequest method can be used to run arbitrary code with the privilege of the user running the browser, which could enable a possible hacker to install malware. [MFSA-2006-24] Claus J�rgensen reported that a text input box can be pr [...] Solution : http://www.debian.org/security/2006/dsa-1051 Network Security Threat Level: High Networks Security ID: 15773, 16476, 16476, 16770, 16881, 17516 Vulnerability Assessment Copyright: This script is (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
Lot of 5 Cisco 10G SFP+ 850nm 300m Transceiver Module P/N: SFP-10G-SR-10-2415-03
$15.00
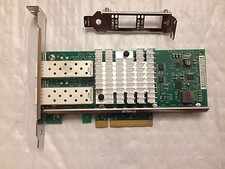
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
|
||
|
No Discussions have been posted on this vulnerability. |