|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA1030] DSA-1030-1 moodle Vulnerability Assessment Details
|
[DSA1030] DSA-1030-1 moodle |
||
|
DSA-1030-1 moodle Detailed Explanation for this Vulnerability Assessment Several vulnerabilities have been discovered in libphp-adodb, the 'adodb' database abstraction layer for PHP, which is embedded in moodle, a course management system for online learning. The Common Vulnerabilities and Exposures project identifies the following problems: Andreas Sandblad discovered that improper user input sanitisation results in a potential remote SQL injection vulnerability enabling a possible hacker to compromise applications, access or modify data, or exploit vulnerabilities in the underlying database implementation. This requires the MySQL root password to be empty. It is fixed by limiting access to the script in question. A dynamic code evaluation vulnerability permits remote attackers to execute arbitrary PHP functions via the 'do' parameter. Andy Staudacher discovered an SQL injection vulnerability due to insufficient input sanitising that permits remote attackers to execute arbitrary SQL commands. GulfTech Security Research discovered multiple cross-site scripting vulnerabilities due to improper user-supplied input sanitisation. Attackers can exploit these vulnerabilities to cause arbitrary scripts to be executed in the browser of an unsuspecting user's machine, or result in the theft of cookie-based authentication credentials. The old stable distribution (woody) does not contain moodle packages. For the stable distribution (sarge) these problems have been fixed in version 1.4.4.dfsg.1-3sarge1. For the unstable distribution these problems will be fixed soon. We recommend that you upgrade your moodle package. Solution : http://www.debian.org/security/2006/dsa-1030 Network Security Threat Level: High Networks Security ID: 16187, 16364, 16720 Vulnerability Assessment Copyright: This script is (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

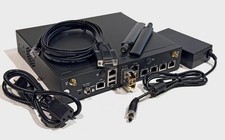
OPNsense pfSense 8-Core Atom C3758 2.2GHz 8GB DDR4 64GB SSD 8x NIC QAT AES VPN
$115.00
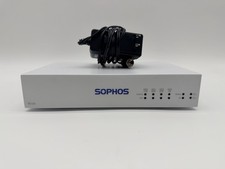
Sophos SG 115 rev.3 Firewall Security Appliance SG1153BAEUS + OPNsense
$85.00
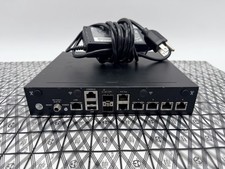
pfSense Firewall 16-Core Atom C3958 8GB DDR4 RAM 64GB SSD 8x 1Gbe QAT AES-NI VPN
$184.99
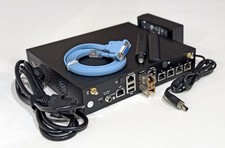
OPNsense pfSense 16-Core Atom C3958 16GB ECC RAM 512GB SSD 8-Port QAT AES-NI VPN
$248.00
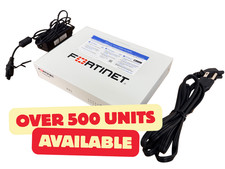
Fortinet FortiGate 60F FG-60F P24286-03-13 Network Firewall Security Appliance
$155.75
Palo Alto PA-220 Next-Gen Firewall 520-000309-00J
$40.00
Fortinet FortiGate 60F FG-60F UTM UTP License Until 2027 Network Security FW VPN
$219.99
Firewalla Purple SE Cyber Security Firewall Home Business VPN…
$215.00
SonicWall TZ280 Firewall 03-SSC-6933 Advanced Edition 3YR NEW SEALED
$999.99
NETGEAR ProSafe 8-Port Gigabit VPN Firewall FVS318G NEW IN BOX
$69.99
|
||
|
No Discussions have been posted on this vulnerability. |