|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA073] DSA-073-1 imp Vulnerability Assessment Details
|
[DSA073] DSA-073-1 imp |
||
|
DSA-073-1 imp Detailed Explanation for this Vulnerability Assessment The Horde team released version 2.2.6 of IMP (a web based IMAP mail program) which fixes three security problems. Their release announcement describes them as follows: A PHPLIB vulnerability permited a possible hacker to provide a value for the array element $_PHPLIB[libdir], and thus to get scripts from another server to load and execute. This vulnerability is remotely exploitable. (Horde 1.2.x ships with its own customized version of PHPLIB, which has now been patched to prevent this problem.) By using tricky encodings of "javascript:" a possible hacker can cause malicious JavaScript code to execute in the browser of a user reading email sent by attacker. (IMP 2.2.x already filters many such patterns several new ones that were slipping past the filters are now blocked.) A hostile user that can create a publicly-readable file named "prefs.lang" somewhere on the Apache/PHP server can cause that file to be executed as PHP code. The IMP configuration files could thus be read, the Horde database password used to read and alter the database used to store contacts and preferences, etc. We do not believe this is remotely exploitable directly through Apache/PHP/IMP however, shell access to the server or other means (e.g., FTP) could be used to create this file. This has been fixed in version 2:2.2.6-0.potato.1. Please note that you will also need to upgrade the horde package to the same version. Solution : http://www.debian.org/security/2001/dsa-073 Network Security Threat Level: High Networks Security ID: 3082, 3083 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

GIGABYTE A520M DS3H AC AMD AM4 Motherboard mATX
$59.99
GIGABYTE Z790 AORUS ELITE AX LGA 1700 Intel Z790 ATX Motherboard with DDR5
$189.99
Intel H310 LGA1151 8-9th Gen DDR4 M.2 NVMe mATX Motherboard IO Shield Battery
$54.99
ASUS PRIME Z490-V Motherboard Intel Z490 10th gen DDR4 LGA 1200 ATX w/ IO Shield
$84.99
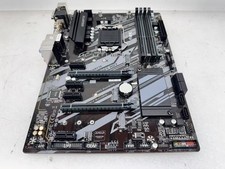
GIGABYTE B365 HD3 LGA1151 Intel 9th Gen motherboard
$59.99
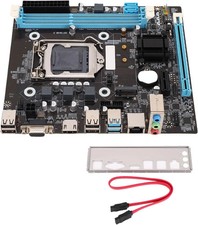
Intel H81 Motherboard M.2 NVMe LGA 1150 mATX w/ IO Shield (Random Slot Color)
$29.90
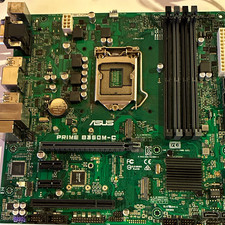
ASUS PRIME B360M-C MicroATX Intel LGA1151 DDR4 HDMI VGA USB RJ-45 Audio
$34.99
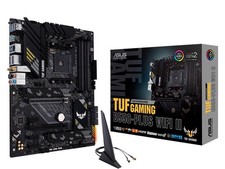
ASUS TUF GAMING B550-PLUS WIFI II AM4 AMD B550 ATX AMD Motherboard
$95.99
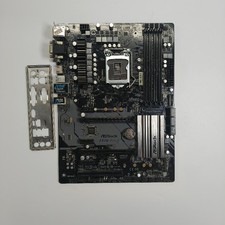
ASRock Z370 Pro4 LGA 1151 Z370 HDMI USB 3.1 2 Ultra M.2 DDR4 ATX Motherboard
$75.00
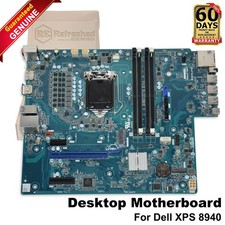
Dell XPS 8940 Desktop Motherboard Intel H470 LGA1200 DDR4 K3CM7 KV3RP 427JK
$154.99
|
||
|
No Discussions have been posted on this vulnerability. |