|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA047] DSA-047-1 kernel Vulnerability Assessment Details
|
[DSA047] DSA-047-1 kernel |
||
|
DSA-047-1 kernel Detailed Explanation for this Vulnerability Assessment The kernels used in Debian GNU/Linux 2.2 have been found to have multiple security problems. This is a list of problems based on the 2.2.19 release notes as found on http://www.linux.org.uk/: binfmt_misc used user pages directly the CPIA driver had an off-by-one error in the buffer code which made it possible for users to write into kernel memory the CPUID and MSR drivers had a problem in the module unloading code which could cause a system crash if they were set to automatically load and unload (please note that Debian does not automatically unload kernel modules) There was a possible hang in the classifier code The getsockopt and setsockopt system calls did not handle sign bits correctly which made a local DoS and other attacks possible The sysctl system call did not handle sign bits correctly which permited a user to write in kernel memory ptrace/exec races that could give a local user extra rights possible abuse of a boundary case in the sockfilter code SYSV shared memory code could overwrite recently freed memory which might cause problems The packet length checks in the masquerading code were a bit lax (probably not exploitable) Some x86 assembly bugs caused the wrong number of bytes to be copied. A local user could deadlock the kernel due to bugs in the UDP port allocation. All these problems are fixed in the 2.2.19 kernel, and it is highly recommend that you upgrade machines to this kernel. Please note that kernel upgrades are not done automatically. You will have to explicitly tell the packaging system to install the right kernel for your system. Solution : http://www.debian.org/security/2001/dsa-047 Network Security Threat Level: High Networks Security ID: 2529 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Windows XP, Vista, 8.1, Linux Knoppix, Office XP, (6 CDS)
$10.00
KNOPPIX 9.1 Linux Install & Live DVD 32bit & 64bit
$19.99
KNOPPIX USB DVD OS , BEST OF ALL HIGHLY RECOMENDED
$11.99
Knoppix Live GNU Linux System 9.1 on Bootable CD / DVD / USB Flash Drive
$5.99
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 16G USB Stick
$20.85
$8.00

VINTAGE SOFTWARE | KNOPPIX STD 0.1 (SECURITY TOOLS DISTRIBUTION)
$7.57
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 32G USB Stick
$21.42
$7.00
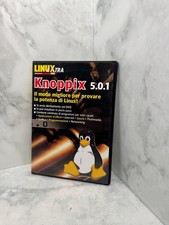
Knoppix 5.0.1 ULTRA RARE Linux DVD - Linux Pro Extra August 2006
$33.98
|
||
|
No Discussions have been posted on this vulnerability. |