|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA043] DSA-043-1 zope Vulnerability Assessment Details
|
[DSA043] DSA-043-1 zope |
||
|
DSA-043-1 zope Detailed Explanation for this Vulnerability Assessment This advisory covers several vulnerabilities in Zope that have been addressed. Hotfix 08_09_2000 "Zope security alert and hotfix product" The issue involves the fact that the getRoles method of user objects contained in the default UserFolder implementation returns a mutable Python type. Because the mutable object is still associated with the persistent User object, users with the ability to edit DTML could arrange to give themselves extra roles for the duration of a single request by mutating the roles list as a part of the request processing. Hotfix 2000-10-02 "ZPublisher security update" It is sometimes possible to access, through a URL only, objects protected by a role which the user has in some context, but not in the context of the accessed object. Hotfix 2000-10-11 "ObjectManager subscripting" The issue involves the fact that the 'subscript notation' that can be used to access items of ObjectManagers (Folders) did not correctly restrict return values to only actual sub items. This made it possible to access names that should be private from DTML (objects with names beginning with the underscore '_' character). This could permit DTML authors to see private implementation data structures and in certain cases possibly call methods that they shouldn't have access to from DTML. Hotfix 2001-02-23 "Class attribute access" The issue is related to ZClasses in that a user with through-the-web scripting capabilities on a Zope site can view and assign class attributes to ZClasses, possibly permiting them to make inappropriate changes to ZClass instances. A second part fixes problems in the ObjectManager, PropertyManager, and PropertySheet classes related to mutability of method return values which could be perceived as a security problem. These fixes are included in zope 2.1.6-7 for Debian 2.2 (potato). We recommend you upgrade your zope package immediately. Solution : http://www.debian.org/security/2001/dsa-043 Network Security Threat Level: High Networks Security ID: 2458 Vulnerability Assessment Copyright: This script is (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
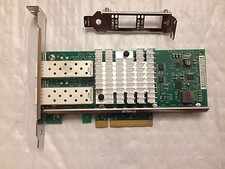
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
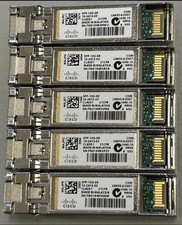
Lot of 5 Cisco 10G SFP+ 850nm 300m Transceiver Module P/N: SFP-10G-SR-10-2415-03
$15.00
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
|
||
|
No Discussions have been posted on this vulnerability. |