|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gain a shell remotely >> CUPS < 1.1.23 Multiple Vulnerabilities Vulnerability Assessment Details
|
CUPS < 1.1.23 Multiple Vulnerabilities |
||
|
Checks version of CUPS Detailed Explanation for this Vulnerability Assessment The remote host is running a CUPS server whose version number is between 1.0.4 and 1.1.22 inclusive. Such versions are prone to multiple vulnerabilities : - A remotely exploitable buffer overflow in the 'hpgltops' filter that enable specially crafted HPGL files can execute arbitrary commands as the CUPS 'lp' account. - A local user may be able to prevent anyone from changing his or her password until a temporary copy of the new password file is cleaned up ('lppasswd' flaw). - A local user may be able to add arbitrary content to the password file by closing the stderr file descriptor while running lppasswd (lppasswd flaw). - A local attacker may be able to truncate the CUPS password file, thereby denying service to valid clients using digest authentication. (lppasswd flaw). - The application applys ACLs to incoming print jobs in a case-sensitive fashion. Thus, a possible hacker can bypass restrictions by changing the case in printer names when submitting jobs. [Fixed in 1.1.21.] ***** Nessus has acertaind the vulnerability exists simply ***** by looking at the version number of CUPS installed on ***** the remote host. See also : http://www.cups.org/str.php?L700 http://www.cups.org/str.php?L1024 http://www.cups.org/str.php?L1023 Solution : Upgrade to CUPS 1.1.23 or later. Network Security Threat Level: High Networks Security ID: 11968, 12004, 12005, 12007, 12200, 14265 Vulnerability Assessment Copyright: This script is Copyright (C) 2005 George A. Theall |
||
|
Cables, Connectors |

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
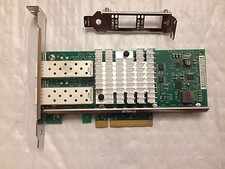
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
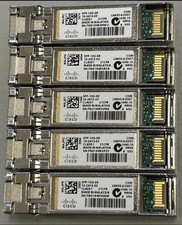
Lot of 5 Cisco 10G SFP+ 850nm 300m Transceiver Module P/N: SFP-10G-SR-10-2415-03
$15.00
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
|
||
|
No Discussions have been posted on this vulnerability. |