|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gain root remotely >> Brightmail AntiSpam bmagent Multiple Vulnerabilities Vulnerability Assessment Details
|
Brightmail AntiSpam bmagent Multiple Vulnerabilities |
||
|
Tries to read a local file using Brightmail Agent Detailed Explanation for this Vulnerability Assessment Summary : The remote web server is affected by multiple vulnerabilities. Description : The remote host is running Brightmail AntiSpam, an anti-spam and anti- virus filter for mail servers, and includes Brightmail Agent, a web server intended to be used by a Brightmail Control Center to manage the Brightmail Scanner. The version of Brightmail Agent installed on the remote host does not require authentication and thus permits attackers to gain administrative control of the affected application. A possible hacker can exploit this issue to stop or disable the Brightmail Scanner's services, which could disrupt mail delivery for legitimate users or to read and write to files associated with the application, which could result in the disclosure of sensitive information or reconfiguration of the application itself. In addition, the Brightmail Agent suffers from a directory traversal vulnerability such that reads and writes are not limited to the application's directory. Successful exploitation of this issue may result in a complete compromise of the affected host since, under Windows, the application runs with LOCAL SYSTEM rights. See also : http://securityresponse.symantec.com/avcenter/security/Content/2006.07.27.html Solution : Either restrict access to Brightmail Agent (refer to document id 2004123109522163 in Symantec's Support Knowledge Base) or upgrade to Symantec Brightmail AntiSpam 6.0.4 / Symantec Mail Security for SMTP 5.0 or later. Network Security Threat Level: Medium / CVSS Base Score : 4.7 (AV:R/AC:L/Au:NR/C:P/I:P/A:N/B:N) Networks Security ID: 19182 Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |


Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$379.00

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99

Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
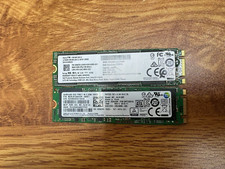
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
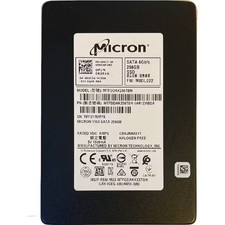
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00

Netac 256GB SSD 2.5'' SATA III 6Gb/s Internal Solid State Drive 500MB/s PC/Latop
$40.00
|
||
|
No Discussions have been posted on this vulnerability. |