|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Windows >> Blackmoon FTP stores passwords in cleartext Vulnerability Assessment Details
|
Blackmoon FTP stores passwords in cleartext |
||
|
Acertains the presence of Blackmoon ftp users database Detailed Explanation for this Vulnerability Assessment The remote host has the program BlackMoon FTP installed. There is a design issue in the program which makes it store the username and password of the FTP server in cleartext in the file 'blackmoon.mdb' Any user with an account on this host may read this file and use the password to connect to this FTP server. Solution : None Risk : Low Networks Security ID: 7646 Vulnerability Assessment Copyright: This script is Copyright (C) 2003 Tenable Network Security |
||
|
Cables, Connectors |

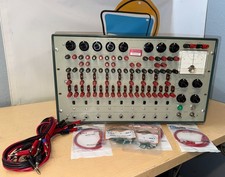
Refurbished Working 1960's Heathkit EC-1 Educational Electronic Analog Computer
$2999.99
Vintage George A Philbrick Researches Tube Analog Computer Module Serial 005503
$109.99
1969 EAI TR-20 Analog Computer Programming PACE Philbrick Electronic Associates
$36.00
Vintage 1970’s Analogic MP2110 10-Bit A/D Converter Computer Circuit Board
$24.99
Extron RGB-160XI Analog Computer Video 60-378-01
$127.06
Vintage Goodyear Electronic GEDA Analog Computer Plug -- Extremely Rare
$179.00
VINTAGE 1970s SKIT Scientific Kit for Computer & Electronics SEALED INSIDE Rare
$380.00
Vintage Analog Computing Magazines For Atari Computer Owners No 11-20 Acceptable
$75.00
VINTAGE Apple Unidisk Analog Card - Circa 1986 | P/N 820-0190-A
$22.67
Vintage HP 82166A HP-IL Converter Custom “The BOX” TTL/DAC Interface Controller
$499.99
|
||
|
No Discussions have been posted on this vulnerability. |