|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Denial of Service >> BIND9 DoS Vulnerability Assessment Details
|
BIND9 DoS |
||
|
Checks the remote BIND version Detailed Explanation for this Vulnerability Assessment The remote BIND server, according to its version number, is vulnerable to a denial of service attack. A possible hacker may use this flaw to prevent this service to work properly. Solution : upgrade to bind 9.2.1 Network Security Threat Level: High Networks Security ID: 4936 Vulnerability Assessment Copyright: This script is Copyright (C) 2002 Renaud Deraison |
||
|
Cables, Connectors |

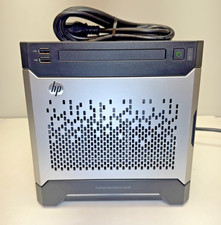
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
Supermicro E200-8D Mini Server Xeon D-1528 6-Core 64GB ECC 1TB SSD 2x10GbE IPMI
$525.00
Supermicro CSE-815-5 4B LFF Xeon E3-1245v6 16GB DDR4 1x 9361-8i 4x 1TB SATA HDD
$483.99
$280.00
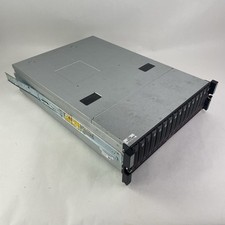
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |