|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Denial of Service >> AnalogX denial of service by long CGI name Vulnerability Assessment Details
|
AnalogX denial of service by long CGI name |
||
|
Crash the remote HTTP service Detailed Explanation for this Vulnerability Assessment It was possible to crash the remote service by requesting a URL with too many characters following the /cgi-bin/ directory. For example: http://www.YOURSERVER.com/cgi-bin/TOO-MANY-CHARACTERS where 'TOO-MANY-CHARACTERS' represents a random string of 8,000 characters. Solution : Upgrade your web server to the latest version, or consider an alternate web server, such as Apache (http://www.apache.org). Network Security Threat Level: High Networks Security ID: 1349 Vulnerability Assessment Copyright: This script is Copyright (C) 2000 Renaud Deraison |
||
|
Cables, Connectors |

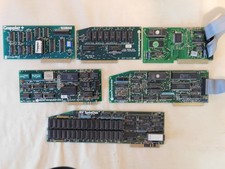
Apple Computer cards VTG 670-8020-B 607-0103-C 607-0291-C AST -Orange Micro ++
$169.00
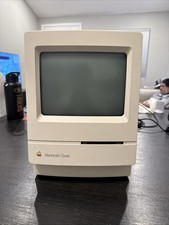
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
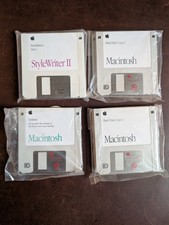
Vintage 1992 Mac System 7.1P1 Apple Software 3.5” Floppy Disks NOS
$35.00
READ - Vintage Apple Macintosh SE/30 - Boots
$850.00
Vintage 1983 Apple II ProDOS User's Kit Computer Software NEW SEALED A2D2010
$64.95
Vintage Apple Computer 3.5 Floppy Drive EMPTY BOX
$29.99
Apple Macintosh Plus 1MB M0001A Vintage Computer - Works
$169.99
Vintage Apple II Avant-Garde Creations Super Shape Draw And Animate 1981
$295.00
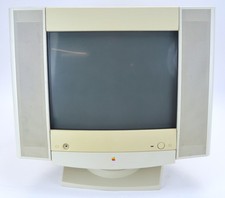
Vintage Apple Multiple Scan 15av Display Monitor M4681
$299.99
Apple cloth fabric banner iBook tangerine orange New Old Stock Vintage
$99.00
|
||
|
No Discussions have been posted on this vulnerability. |